Rank #8 of 8 in Agent Sandboxes & Code Execution
Access
Install
pip install modal vs E2B
 vs Daytona
 vs Cloudflare Sandboxes
 vs Vercel Sandbox
 vs Runloop
 vs Blaxel
 vs Maritime
Showcase
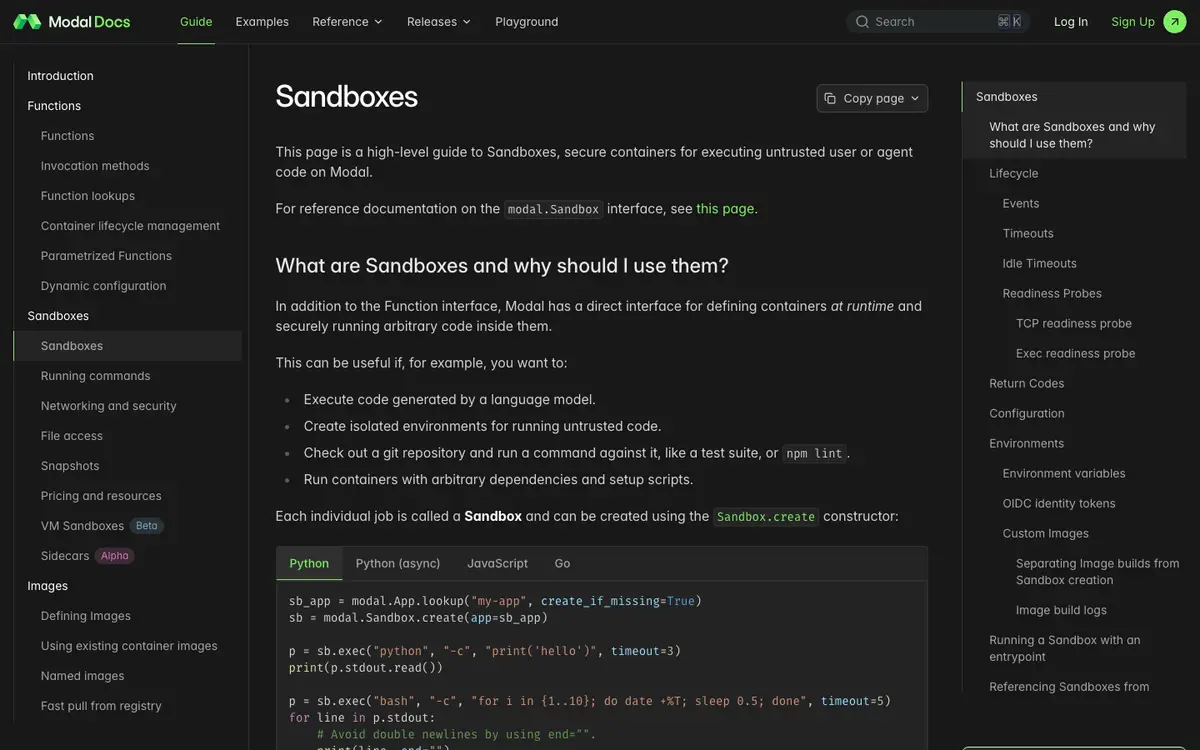
Try itExperimental
See what an agent can do with Modal Sandboxes before you ever sign up. Pick a story: recorded sessions replay real probe-harness transcripts; sandboxed self-drive sessions are designed and gated (docs/TRY-IT.md).
$modal --helprecorded session — replayed, not liveVerified integrations
Connections to other tracked products — hover a chip for the verbatim evidence quote behind it.

By theme — the product's score on each story themeBy theme
Agenticness — how well agents can access and operate the productAgenticnessevidence →
How well agents can access and operate the product
Automation depth — how much of the product can run unattendedAutomation depthevidence →
How much of the product can run unattended
Capabilities hardware — stories about capabilities hardware in this arenaCapabilities hardwareevidence →
Stories about capabilities hardware in this arena
Code execution — stories about code execution in this arenaCode executionevidence →
Stories about code execution in this arena
Dev experience — day-to-day developer experience — setup friction, docs, debugging, iteration speedDev experienceevidence →
Day-to-day developer experience — setup friction, docs, debugging, iteration speed
Isolation security — stories about isolation security in this arenaIsolation securityevidence →
Stories about isolation security in this arena
Openness — open source, data portability, and self-hosting storiesOpennessevidence →
Open source, data portability, and self-hosting stories
Performance scale — stories about performance scale in this arenaPerformance scaleevidence →
Stories about performance scale in this arena
Pricing limits — free-tier ceilings, usage caps, and rate limits before you have to payPricing limitsevidence →
Free-tier ceilings, usage caps, and rate limits before you have to pay
Privacy posture — data-handling and privacy storiesPrivacy postureevidence →
Data-handling and privacy stories
Provisioning lifecycle — creating, updating, and tearing down resources across their lifecycleProvisioning lifecycleevidence →
Creating, updating, and tearing down resources across their lifecycle
Snapshot persistence — stories about snapshot persistence in this arenaSnapshot persistenceevidence →
Stories about snapshot persistence in this arena
Story verdicts — every judged story with its evidenceStory verdicts
What’s free: 0 free · 4 paid · 0 enterprise · 23 not stated in evidence
Follow the green: where the map greys out is where Modal Sandboxes stops today. ✓ full · ~ partial · ! disputed · — none · n/a not applicable.
Agenticness — how well agents can access and operate the productAgenticness
How well agents can access and operate the product
API surface
Drive the product through a documented public API
✓8/10
unlocks → Webhooks · Scoped API keys · MCP server · Machine-readable spec · Versioning policy · Full data export
Subscribe to events via webhooks
—–
Build against official SDKs
✓8/10
Issue scoped/least-privilege API credentials for an agent
—0/10
Connect an agent via an official MCP server
—–
Download a machine-readable API spec (OpenAPI or equivalent)
—0/10
Rely on versioned APIs with a documented deprecation policy
—0/10
Test against a sandbox environment without touching production data
✓7/10
Explore an interactive API reference with runnable examples
—0/10
Docs for agents
Point an agent at llms.txt or agent-oriented docs
✓8/10
Agentic features
Delegate tasks to a built-in AI assistant inside the product
n/an/a
Operate the product with natural-language commands
—0/10
Plug MCP servers into this product so it can use their tools
—–
Get AI-generated insights and suggestions from my data inside the product
n/an/a
Set up automations that run autonomously in the background
~6/10
Automation depth — how much of the product can run unattendedAutomation depth
How much of the product can run unattended
Capabilities hardware — stories about capabilities hardware in this arenaCapabilities hardware
Stories about capabilities hardware in this arena
Code execution — stories about code execution in this arenaCode execution
Stories about code execution in this arena
Dev experience — day-to-day developer experience — setup friction, docs, debugging, iteration speedDev experience
Day-to-day developer experience — setup friction, docs, debugging, iteration speed
Isolation security — stories about isolation security in this arenaIsolation security
Stories about isolation security in this arena
Openness — open source, data portability, and self-hosting storiesOpenness
Open source, data portability, and self-hosting stories
Performance scale — stories about performance scale in this arenaPerformance scale
Stories about performance scale in this arena
Pricing limits — free-tier ceilings, usage caps, and rate limits before you have to payPricing limits
Free-tier ceilings, usage caps, and rate limits before you have to pay
Privacy posture — data-handling and privacy storiesPrivacy posture
Data-handling and privacy stories
Provisioning lifecycle — creating, updating, and tearing down resources across their lifecycleProvisioning lifecycle
Creating, updating, and tearing down resources across their lifecycle
Snapshot persistence — stories about snapshot persistence in this arenaSnapshot persistence
Stories about snapshot persistence in this arena
Sorted by importance (agentic first) (high → low) · 51/51 stories · click a row’s chevron for the rationale and evidence
Drive the product through a documented public API G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 3 | full | 8/10 | Tprobed | |
Connect an agent via an official MCP server G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 3 | none | untested | none yet | |
Delegate tasks to a built-in AI assistant inside the product G Agentic features | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 3 | n/a | untested | none yet | |
Plug MCP servers into this product so it can use their tools G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 3 | none | untested | none yet | |
Build against official SDKs G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | full | 8/10 | Xcommunity | |
Point an agent at llms.txt or agent-oriented docs G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | full | 8/10 | Tprobed | |
Run the product headlessly / in CI for automation G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | full | 8/10 | Tprobed | |
Use an official CLI G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | full | 8/10 | Tprobed | |
Set up automations that run autonomously in the background G Agentic features | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | partial | 6/10 | Xcommunity | |
Download a machine-readable API spec (OpenAPI or equivalent) G Api quality | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | none | 0/10 | ||
Explore an interactive API reference with runnable examples G Api quality | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | none | 0/10 | ||
Issue scoped/least-privilege API credentials for an agent G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | none | 0/10 | ||
Operate the product with natural-language commands G Agentic features | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | none | 0/10 | ||
Rely on versioned APIs with a documented deprecation policy G Api quality | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | none | 0/10 | ||
Get AI-generated insights and suggestions from my data inside the product G Agentic features | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | n/a | untested | none yet | |
Subscribe to events via webhooks G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | none | untested | none yet | |
Test against a sandbox environment without touching production data G Api quality | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 1 | full | 7/10 | Tprobed | |
Execute untrusted, AI-generated code without risking my own infrastructure C Untrusted code | developer | Code execution — stories about code execution in this arenaCode execution | 3 | full | 8/10 | Tprobed | |
My agent can provision its own sandbox, execute code, read the results, and tear it down — end to end without a human C Agent lifecycle | ai-native user | Dev experience — day-to-day developer experience — setup friction, docs, debugging, iteration speedDev experience | 3 | full | 8/10 | Tprobed | |
Pay per second only for the compute a sandbox actually uses G Pricing | platform-engineer | Pricing limits — free-tier ceilings, usage caps, and rate limits before you have to payPricing limits | 3 | fullpaid | 8/10 | Xcommunity | |
Spin up an isolated sandbox with one API/SDK call and get a live environment in seconds C Lifecycle | developer | Provisioning lifecycle — creating, updating, and tearing down resources across their lifecycleProvisioning lifecycle | 3 | full | 8/10 | Tprobed | |
Rely on a documented hard isolation boundary (microVM or equivalent) between sandboxes and my systems C Isolation | platform-engineer | Isolation security — stories about isolation security in this arenaIsolation security | 3 | partial | 5/10 | Tprobed | |
Restrict or allow the sandbox's network egress with explicit policy C Network policy | platform-engineer | Isolation security — stories about isolation security in this arenaIsolation security | 3 | partial | 5/10 | Tprobed | |
Run large concurrent fleets of sandboxes with documented concurrency limits C Scale | platform-engineer | Performance scale — stories about performance scale in this arenaPerformance scale | 3 | partialpaid | 5/10 | Xcommunity | |
Snapshot a sandbox and later restore or fork new sandboxes from that snapshot C Snapshots | developer | Snapshot persistence — stories about snapshot persistence in this arenaSnapshot persistence | 3 | partial | 5/10 | Cclaimed | |
Start sandboxes with documented sub-second-to-few-second cold starts C Latency | developer | Performance scale — stories about performance scale in this arenaPerformance scale | 3 | partial | 4/10 | Cclaimed | |
Define rules that trigger actions automatically on events G | ai-native user | Automation depth — how much of the product can run unattendedAutomation depth | 3 | none | untested | none yet | |
Export all of my data in open formats and leave G | ai-native user | Openness — open source, data portability, and self-hosting storiesOpenness | 3 | none | untested | none yet | |
Prevent my data from being used to train AI models G | ai-native user | Privacy posture — data-handling and privacy storiesPrivacy posture | 3 | n/a | untested | none yet | |
Self-host the core product G | ai-native user | Openness — open source, data portability, and self-hosting storiesOpenness | 3 | none | untested | none yet | |
Run arbitrary shell commands and install packages inside the sandbox C Untrusted code | developer | Code execution — stories about code execution in this arenaCode execution | 2 | full | 9/10 | Tprobed | |
Attach GPUs to sandboxed workloads C Workloads | developer | Capabilities hardware — stories about capabilities hardware in this arenaCapabilities hardware | 2 | fullpaid | 8/10 | Xcommunity | |
Define custom sandbox templates or bring my own container image C Runtimes | developer | Code execution — stories about code execution in this arenaCode execution | 2 | full | 8/10 | Xcommunity | |
Read, write, upload, and download files in the sandbox filesystem via the SDK C Files | developer | Code execution — stories about code execution in this arenaCode execution | 2 | full | 8/10 | Tprobed | |
Do everything through the API that I can do in the UI G | ai-native user | Openness — open source, data portability, and self-hosting storiesOpenness | 2 | partial | 6/10 | Tprobed | |
Execute code in multiple language runtimes (Python, JavaScript, and more) and get rich results back C Runtimes | developer | Code execution — stories about code execution in this arenaCode execution | 2 | partial | 6/10 | Cclaimed | |
Perform bulk operations across many items at once G | ai-native user | Automation depth — how much of the product can run unattendedAutomation depth | 2 | partialpaid | 6/10 | Xcommunity | |
Give an agent a sandbox where host secrets and credentials are unreachable by the code it runs C Isolation | ai-native user | Isolation security — stories about isolation security in this arenaIsolation security | 2 | partial | 5/10 | Tprobed | |
Keep a sandbox session running for hours or days for long agent tasks C Scale | developer | Performance scale — stories about performance scale in this arenaPerformance scale | 2 | partial | 5/10 | Xcommunity | |
Pause a running sandbox and resume it later with filesystem and memory state intact C Snapshots | developer | Snapshot persistence — stories about snapshot persistence in this arenaSnapshot persistence | 2 | partial | 4/10 | Cclaimed | |
Expose a port from the sandbox on a public preview URL to reach services running inside C Preview access | developer | Provisioning lifecycle — creating, updating, and tearing down resources across their lifecycleProvisioning lifecycle | 2 | partial | 3/10 | Tprobed | |
Read the product's source under an open license G | ai-native user | Openness — open source, data portability, and self-hosting storiesOpenness | 2 | none | 0/10 | ||
Schedule recurring jobs or workflows G | ai-native user | Automation depth — how much of the product can run unattendedAutomation depth | 2 | none | 0/10 | ||
Choose where my data is stored (region/residency) G | ai-native user | Privacy posture — data-handling and privacy storiesPrivacy posture | 2 | none | untested | none yet | |
Control data retention and deletion G | ai-native user | Privacy posture — data-handling and privacy storiesPrivacy posture | 2 | none | untested | none yet | |
Opt out of telemetry and usage tracking G | ai-native user | Privacy posture — data-handling and privacy storiesPrivacy posture | 2 | none | untested | none yet | |
Run a headless browser or full desktop environment inside the sandbox C Workloads | developer | Capabilities hardware — stories about capabilities hardware in this arenaCapabilities hardware | 2 | none | untested | none yet | |
Run coding agents like Claude Code or Codex inside the sandbox following the vendor's own recipe C Agent workloads | ai-native user | Capabilities hardware — stories about capabilities hardware in this arenaCapabilities hardware | 2 | none | untested | none yet | |
Set timeouts so sandboxes shut down automatically and stop billing when idle or done G Lifecycle | developer | Provisioning lifecycle — creating, updating, and tearing down resources across their lifecycleProvisioning lifecycle | 2 | none | untested | none yet | |
Start building with a free tier or included credits without talking to sales G Pricing | developer | Pricing limits — free-tier ceilings, usage caps, and rate limits before you have to payPricing limits | 1 | none | untested | none yet | |
Version, review, and roll back my automations G | ai-native user | Automation depth — how much of the product can run unattendedAutomation depth | 1 | none | untested | none yet |
Opportunities — the stories that would move this product's scores, from its own judged verdictsOpportunitiestop 8 of 34 stories with headroom
What would move Modal Sandboxes’s scores — derived from its own judged verdicts, biggest headroom first. Each line quotes what the judge found missing; shipping it (or evidencing it publicly) is the fix.
Agenticness — how well agents can access and operate the productPlug MCP servers into this product so it can use their tools
nonemoves agent-readyimpact 45
The axis applies to this product kind (peer products hold positive or none verdicts on this story), so lack of evidence for an applicable capability is "none", never "na".
Agenticness — how well agents can access and operate the productConnect an agent via an official MCP server
nonemoves agent-readyimpact 45
The axis applies to this product kind (peer products hold positive or none verdicts on this story), so lack of evidence for an applicable capability is "none", never "na".
Automation depth — how much of the product can run unattendedDefine rules that trigger actions automatically on events
nonemoves PA Scoreimpact 30
The evidence describes Modal Sandboxes as a programmatic, on-demand execution environment for untrusted/agent code, but nothing in the pack shows a rules/trigger engine that fires actions automatically on external events (e.g., webhooks, event-driven policies).
Openness — open source, data portability, and self-hosting storiesExport all of my data in open formats and leave
nonemoves PA Scoreimpact 30
The axis applies to this product kind (peer products hold positive or none verdicts on this story), so lack of evidence for an applicable capability is "none", never "na".
Openness — open source, data portability, and self-hosting storiesSelf-host the core product
nonemoves PA Scoreimpact 30
Modal is a fully-managed cloud platform for running Sandboxes; there is no evidence of any self-hostable/on-prem version of the core product, and everything described (pay-per-second billing, GPU access, hosted CLI) implies a proprietary SaaS deployment model only.
Agenticness — how well agents can access and operate the productOperate the product with natural-language commands
nonemoves Built-in AIimpact 30
Modal Sandboxes is controlled exclusively via SDK (Python/JS/Go) calls and a traditional CLI (modal run, modal shell, etc.); there is no evidence of a natural-language command interface or chat-driven control layer for operating sandboxes.
Agenticness — how well agents can access and operate the productIssue scoped/least-privilege API credentials for an agent
nonemoves agent-readyimpact 30
Missing: any documented API/credential-scoping mechanism, permission granularity docs, or examples of issuing least-privilege tokens to agents.
Agenticness — how well agents can access and operate the productSubscribe to events via webhooks
nonemoves agent-readyimpact 30
No evidence anywhere in the pack of a webhook subscription mechanism or event-driven notification system for Modal Sandboxes; the docs focus on programmatic spin-up, execution, logging, and filesystem access, not outbound event/webhook subscriptions.
Showing the top 8 of 34 — every none/partial verdict in the story verdicts table is headroom.
Think a verdict is wrong? Every verdicts-table row has a Flag link — see the methodology.
Coverage map — which docs area, API section, or community source covers which judged storiesCoverage map7 surfaces · 27 covered stories
Where the cited evidence behind each covered verdict came from — the same citations the verdicts table shows, no extra judging.
docs24 stories
- Point an agent at llms.txt or agent-oriented docs
- Run the product headlessly / in CI for automation
- Use an official CLI
- Drive the product through a documented public API
- Build against official SDKs
- Set up automations that run autonomously in the background
- Test against a sandbox environment without touching production data
- Read, write, upload, and download files in the sandbox filesystem via the SDK
- Define custom sandbox templates or bring my own container image
- Execute code in multiple language runtimes (Python, JavaScript, and more) and get rich results back
- Execute untrusted, AI-generated code without risking my own infrastructure
- Run arbitrary shell commands and install packages inside the sandbox
- My agent can provision its own sandbox, execute code, read the results, and tear it down — end to end without a human
- Rely on a documented hard isolation boundary (microVM or equivalent) between sandboxes and my systems
- Give an agent a sandbox where host secrets and credentials are unreachable by the code it runs
- Restrict or allow the sandbox's network egress with explicit policy
- Do everything through the API that I can do in the UI
- Start sandboxes with documented sub-second-to-few-second cold starts
- Run large concurrent fleets of sandboxes with documented concurrency limits
- Keep a sandbox session running for hours or days for long agent tasks
- Spin up an isolated sandbox with one API/SDK call and get a live environment in seconds
- Expose a port from the sandbox on a public preview URL to reach services running inside
- Pause a running sandbox and resume it later with filesystem and memory state intact
- Snapshot a sandbox and later restore or fork new sandboxes from that snapshot
modal.com16 stories
- Run the product headlessly / in CI for automation
- Set up automations that run autonomously in the background
- Test against a sandbox environment without touching production data
- Perform bulk operations across many items at once
- Attach GPUs to sandboxed workloads
- Define custom sandbox templates or bring my own container image
- Execute code in multiple language runtimes (Python, JavaScript, and more) and get rich results back
- Execute untrusted, AI-generated code without risking my own infrastructure
- Run arbitrary shell commands and install packages inside the sandbox
- My agent can provision its own sandbox, execute code, read the results, and tear it down — end to end without a human
- Give an agent a sandbox where host secrets and credentials are unreachable by the code it runs
- Start sandboxes with documented sub-second-to-few-second cold starts
- Run large concurrent fleets of sandboxes with documented concurrency limits
- Keep a sandbox session running for hours or days for long agent tasks
- Pay per second only for the compute a sandbox actually uses
- Spin up an isolated sandbox with one API/SDK call and get a live environment in seconds
Hacker News15 stories
- Run the product headlessly / in CI for automation
- Drive the product through a documented public API
- Build against official SDKs
- Set up automations that run autonomously in the background
- Test against a sandbox environment without touching production data
- Perform bulk operations across many items at once
- Attach GPUs to sandboxed workloads
- Define custom sandbox templates or bring my own container image
- Execute untrusted, AI-generated code without risking my own infrastructure
- Run arbitrary shell commands and install packages inside the sandbox
- My agent can provision its own sandbox, execute code, read the results, and tear it down — end to end without a human
- Run large concurrent fleets of sandboxes with documented concurrency limits
- Keep a sandbox session running for hours or days for long agent tasks
- Pay per second only for the compute a sandbox actually uses
- Spin up an isolated sandbox with one API/SDK call and get a live environment in seconds
GitHub README4 stories
OpenAPI spec2 stories
Probe proofs — replayable recordings from the probe harnessProbe proofs
Replayable recordings from our probe harness — see the Prove-It protocol to submit one.
$modal --helpreproduced$ modal --help Usage: modal [OPTIONS] COMMAND [ARGS]... Modal is the fastest way to run code in the cloud. See the website at https://modal.com/ for documentation and more information about running code on Modal. Commands curl Send an authenticated request to a Modal endpoint. deploy Deploy a Modal application. serve Expose Web Functions with hot-reloading on code changes. shell Run a command or interactive shell inside a Modal container. run Run a Modal function or local entrypoint. Deployments app Manage deployed and running apps. container Manage and connect to running containers. endpoint Create and manage LLM inference endpoints. Storage image Manage Images. dict Manage `modal.Dict` objects and inspect their contents. secret Manage secrets. queue Manage `modal.Queue` objects and inspect their contents. volume Read and edit `modal.Volume` volumes. Onboarding setup Bootstrap Modal's configuration. bootstrap Initialize a sample Modal App. Configuration workspace Interact with the current Modal Workspace. environment Create and interact with Environments profile Switch between Modal profiles. config Manage client configuration for the current profile. [redacted] Manage [redacted]s. skills Install and update Modal's agent skills. Observability billing View workspace billing information. changelog Fetch release notes from the Modal changelog. dashboard Open the Modal Dashboard in a web browser.
$modal --versionreproduced$ modal --version modal client version: 1.5.5
Claims vs evidence — vendor claims reconciled against independent verdictsClaims vs evidence
13 of 15 testable claims verified · 0 contradicted → integrity 87/100
15 distinct capability claims found in Modal Sandboxes’s own claimed-docs/GitHub materials, reconciled against our judge’s independent verdicts.
13
Verified
2
Unverified
0
Contradicted
12
Undersold
Verified (15)
“Run untrusted, AI-generated code inside secure, ephemeral sandboxes”
Execute untrusted, AI-generated code without risking my own infrastructurefullproof ↗
“Run untrusted, AI-generated code inside secure, ephemeral sandboxes”
Rely on a documented hard isolation boundary (microVM or equivalent) between sandboxes and my systemspartialproof ↗
“Programmatically spin up fresh isolated sandboxes with custom images and any dependency”
Spin up an isolated sandbox with one API/SDK call and get a live environment in secondsfullproof ↗
“Programmatically spin up fresh isolated sandboxes with custom images and any dependency”
Define custom sandbox templates or bring my own container imagefullproof ↗
“Give autonomous agents a full isolated dev environment preloaded with tools, context, and credentials”
My agent can provision its own sandbox, execute code, read the results, and tear it down — end to end without a humanfullproof ↗
“Spin up hundreds of thousands of concurrent rollout environments within seconds”
Run large concurrent fleets of sandboxes with documented concurrency limitspartialproof ↗
“Attach on-demand H100/A100/A10G GPUs to sandboxes and scale to thousands of concurrent runs”
“Attach on-demand H100/A100/A10G GPUs to sandboxes and scale to thousands of concurrent runs”
Run large concurrent fleets of sandboxes with documented concurrency limitspartialproof ↗
“Pay only for compute used, bursting resources without pre-allocating CPU or memory”
Pay per second only for the compute a sandbox actually usesfullproof ↗
“Sandboxes support filesystem access for reading and writing files”
Read, write, upload, and download files in the sandbox filesystem via the SDKfullproof ↗
“Offers networking and security controls for sandboxes”
Restrict or allow the sandbox's network egress with explicit policypartialproof ↗
“Beta VM Sandboxes provide an additional isolation layer using virtual machines”
Rely on a documented hard isolation boundary (microVM or equivalent) between sandboxes and my systemspartialproof ↗
“Run shell commands or interactive shells inside a Modal container/sandbox”
Run arbitrary shell commands and install packages inside the sandboxfullproof ↗
“Official JS and Go SDKs let developers use Sandboxes and invoke deployed Functions”
“Manage and reconnect to already-running sandbox containers”
Keep a sandbox session running for hours or days for long agent taskspartialproof ↗
Unverified (2)
“Spin up hundreds of thousands of concurrent rollout environments within seconds”
Start sandboxes with documented sub-second-to-few-second cold startspartialproof ↗
“Sandboxes support snapshotting for later restore or forking”
Snapshot a sandbox and later restore or fork new sandboxes from that snapshotpartialproof ↗
Undersold (12)
Point an agent at llms.txt or agent-oriented docsfullproof ↗
Run the product headlessly / in CI for automationfullproof ↗
Drive the product through a documented public APIfullproof ↗
Set up automations that run autonomously in the backgroundpartialproof ↗
Test against a sandbox environment without touching production datafullproof ↗
Perform bulk operations across many items at oncepartialproof ↗
Execute code in multiple language runtimes (Python, JavaScript, and more) and get rich results backpartialproof ↗
Give an agent a sandbox where host secrets and credentials are unreachable by the code it runspartialproof ↗
Do everything through the API that I can do in the UIpartialproof ↗
Expose a port from the sandbox on a public preview URL to reach services running insidepartialproof ↗
Pause a running sandbox and resume it later with filesystem and memory state intactpartialproof ↗
Claims outside our story set (2)
Real capability claims found in Modal Sandboxes’s own materials, but no story in this arena’s taxonomy covers them yet — that’s feedback on the taxonomy, not a mark against the product.
“Provides integrated logging and full visibility into every function, sandbox, and container”
source ↗“Alpha support for running sidecar containers alongside the main sandbox process”
source ↗
Business model
Per-second usage pricing for CPU, memory, and GPU with free monthly starter credits; the Team plan adds a flat monthly fee on top of usage, enterprise is custom.
pricing ↗Score trend
How this product’s scores have moved as evidence and verdicts are re-derived — a point per change, not per day.
Try Experimental
Run it in the microterminal →Recorded agent sessions — and a live MCP handshake where the vendor ships one.
Flag
⚑ Flag a verdictThink a verdict is wrong? Opens a prefilled GitHub issue — or use the ⚑ next to any verdict above.
For agents
Agent surface uptime llms.txt 100% (30d, checked every 6h since Sep 8 '26)