Rank #1 of 6 in Package & Toolchain Managers
Access
Install
 vs Homebrew
 vs Nix
 vs pnpm
 vs uv
 vs Bun (package manager)
Showcase
Try itExperimental
See what an agent can do with mise before you ever sign up. Pick a story: recorded sessions replay real probe-harness transcripts; sandboxed self-drive sessions are designed and gated (docs/TRY-IT.md).
$mise --versionrecorded session — replayed, not liveVerified integrations
Connections to other tracked products — hover a chip for the verbatim evidence quote behind it.


By theme — the product's score on each story themeBy theme
Agent experience — stories about agent experience in this arenaAgent experienceevidence →
Stories about agent experience in this arena
Agenticness — how well agents can access and operate the productAgenticnessevidence →
How well agents can access and operate the product
Automation depth — how much of the product can run unattendedAutomation depthevidence →
How much of the product can run unattended
Cross platform — stories about cross platform in this arenaCross platformevidence →
Stories about cross platform in this arena
Ecosystem extensibility — stories about ecosystem extensibility in this arenaEcosystem extensibilityevidence →
Stories about ecosystem extensibility in this arena
Install reproducibility — stories about install reproducibility in this arenaInstall reproducibilityevidence →
Stories about install reproducibility in this arena
Migration adoption — stories about migration adoption in this arenaMigration adoptionevidence →
Stories about migration adoption in this arena
Monorepo workspaces — stories about monorepo workspaces in this arenaMonorepo workspacesevidence →
Stories about monorepo workspaces in this arena
Openness — open source, data portability, and self-hosting storiesOpennessevidence →
Open source, data portability, and self-hosting stories
Performance caching — stories about performance caching in this arenaPerformance cachingevidence →
Stories about performance caching in this arena
Privacy posture — data-handling and privacy storiesPrivacy postureevidence →
Data-handling and privacy stories
Security supply chain — stories about security supply chain in this arenaSecurity supply chainevidence →
Stories about security supply chain in this arena
Toolchain management — stories about toolchain management in this arenaToolchain managementevidence →
Stories about toolchain management in this arena
Story verdicts — every judged story with its evidenceStory verdicts
Follow the green: where the map greys out is where mise stops today. ✓ full · ~ partial · ! disputed · — none · n/a not applicable.
Agent experience — stories about agent experience in this arenaAgent experience
Stories about agent experience in this arena
Agenticness — how well agents can access and operate the productAgenticness
How well agents can access and operate the product
API surface
Drive the product through a documented public API
~6/10
unlocks → Machine-readable spec · Versioning policy
Subscribe to events via webhooks
n/an/a
Build against official SDKs
n/an/a
Issue scoped/least-privilege API credentials for an agent
n/an/a
Connect an agent via an official MCP server
n/an/a
Download a machine-readable API spec (OpenAPI or equivalent)
—0/10
Rely on versioned APIs with a documented deprecation policy
—0/10
Test against a sandbox environment without touching production data
n/an/a
Explore an interactive API reference with runnable examples
—0/10
Docs for agents
Point an agent at llms.txt or agent-oriented docs
✓7/10
Agentic features
Delegate tasks to a built-in AI assistant inside the product
n/an/a
Operate the product with natural-language commands
—0/10
Plug MCP servers into this product so it can use their tools
n/an/a
Get AI-generated insights and suggestions from my data inside the product
n/an/a
Set up automations that run autonomously in the background
~4/10
Automation depth — how much of the product can run unattendedAutomation depth
How much of the product can run unattended
Cross platform — stories about cross platform in this arenaCross platform
Stories about cross platform in this arena
Ecosystem extensibility — stories about ecosystem extensibility in this arenaEcosystem extensibility
Stories about ecosystem extensibility in this arena
Install reproducibility — stories about install reproducibility in this arenaInstall reproducibility
Stories about install reproducibility in this arena
Migration adoption — stories about migration adoption in this arenaMigration adoption
Stories about migration adoption in this arena
Monorepo workspaces — stories about monorepo workspaces in this arenaMonorepo workspaces
Stories about monorepo workspaces in this arena
Openness — open source, data portability, and self-hosting storiesOpenness
Open source, data portability, and self-hosting stories
Performance caching — stories about performance caching in this arenaPerformance caching
Stories about performance caching in this arena
See published benchmarks or measured numbers backing the manager's speed claims
—0/10
Install prebuilt binary packages from a cache instead of compiling from source
~6/10
Make CI installs fast with a documented cache-restore setup and offline-capable installs
~4/10
Rely on a shared content-addressable store so the same dependency version is stored once on disk across all projects
—–
Privacy posture — data-handling and privacy storiesPrivacy posture
Data-handling and privacy stories
Security supply chain — stories about security supply chain in this arenaSecurity supply chain
Stories about security supply chain in this arena
Audit installed dependencies for known vulnerabilities directly from the CLI
—–
Turn on protections against malicious packages, such as blocking lifecycle scripts or enforcing a minimum release age
✓8/10
Trust that fetched packages are verified against checksums, signatures, or attestations before they run
✓8/10
Toolchain management — stories about toolchain management in this arenaToolchain management
Stories about toolchain management in this arena
Sorted by importance (agentic first) (high → low) · 54/54 stories · click a row’s chevron for the rationale and evidence
Drive the product through a documented public API G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 3 | partial | 6/10 | Tprobed | |
Connect an agent via an official MCP server G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 3 | n/a | untested | none yet | |
Delegate tasks to a built-in AI assistant inside the product G Agentic features | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 3 | n/a | untested | none yet | |
Plug MCP servers into this product so it can use their tools G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 3 | n/a | untested | none yet | |
Run the product headlessly / in CI for automation G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | full | 8/10 | Xcommunity | |
Use an official CLI G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | full | 8/10 | Tprobed | |
Point an agent at llms.txt or agent-oriented docs G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | full | 7/10 | Tprobed | |
Set up automations that run autonomously in the background G Agentic features | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | partial | 4/10 | Cclaimed | |
Download a machine-readable API spec (OpenAPI or equivalent) G Api quality | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | none± | 0/10 | ||
Explore an interactive API reference with runnable examples G Api quality | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | none | 0/10 | ||
Operate the product with natural-language commands G Agentic features | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | none± | 0/10 | ||
Rely on versioned APIs with a documented deprecation policy G Api quality | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | none | 0/10 | ||
Build against official SDKs G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | n/a± | untested | none yet | |
Get AI-generated insights and suggestions from my data inside the product G Agentic features | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | n/a | untested | none yet | |
Issue scoped/least-privilege API credentials for an agent G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | n/a | untested | none yet | |
Subscribe to events via webhooks G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | n/a | untested | none yet | |
Test against a sandbox environment without touching production data G Api quality | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 1 | n/a | untested | none yet | |
Pin exact versions of packages and tools per project and have the manager respect those pins C Pinning | developer | Install reproducibility — stories about install reproducibility in this arenaInstall reproducibility | 3 | full | 8/10 | Xcommunity | |
Have an agent install and update project dependencies non-interactively, with clear exit codes and errors when something fails C Headless installs | ai-native user | Agent experience — stories about agent experience in this arenaAgent experience | 3 | partial | 6/10 | Cclaimed | |
Install prebuilt binary packages from a cache instead of compiling from source C Binary caching | developer | Performance caching — stories about performance caching in this arenaPerformance caching | 3 | partial | 6/10 | Xcommunity | |
Define rules that trigger actions automatically on events G | ai-native user | Automation depth — how much of the product can run unattendedAutomation depth | 3 | partial | 5/10 | Cclaimed | |
Export all of my data in open formats and leave G | ai-native user | Openness — open source, data portability, and self-hosting storiesOpenness | 3 | partial | 5/10 | Cclaimed | |
Install dependencies from a lockfile and get the exact same resolved versions on every machine C Lockfiles | developer | Install reproducibility — stories about install reproducibility in this arenaInstall reproducibility | 3 | partial | 5/10 | Cclaimed | |
Make CI installs fast with a documented cache-restore setup and offline-capable installs C Ci speed | platform-engineer | Performance caching — stories about performance caching in this arenaPerformance caching | 3 | partial | 4/10 | Xcommunity | |
Audit installed dependencies for known vulnerabilities directly from the CLI C Auditing | platform-engineer | Security supply chain — stories about security supply chain in this arenaSecurity supply chain | 3 | none | untested | none yet | |
Manage many packages in one monorepo with workspaces sharing a single lockfile and cross-linked local dependencies C Workspaces | developer | Monorepo workspaces — stories about monorepo workspaces in this arenaMonorepo workspaces | 3 | n/a | untested | none yet | |
Prevent my data from being used to train AI models G | ai-native user | Privacy posture — data-handling and privacy storiesPrivacy posture | 3 | n/a | untested | none yet | |
Self-host the core product G | ai-native user | Openness — open source, data portability, and self-hosting storiesOpenness | 3 | n/a | untested | none yet | |
Install and switch language runtimes or tool versions per project from a checked-in config file C Runtimes | developer | Toolchain management — stories about toolchain management in this arenaToolchain management | 2 | full | 9/10 | Xcommunity | |
Bootstrap a fresh clone with one command that installs everything the project declares C Bootstrap | developer | Install reproducibility — stories about install reproducibility in this arenaInstall reproducibility | 2 | full | 8/10 | Xcommunity | |
Install almost anything I need from a large, actively maintained package registry or repository C Registry | developer | Ecosystem extensibility — stories about ecosystem extensibility in this arenaEcosystem extensibility | 2 | full | 8/10 | Xcommunity | |
Keep using familiar commands and interface conventions from the incumbent tool while adopting this manager C Compatibility | switcher | Migration adoption — stories about migration adoption in this arenaMigration adoption | 2 | full | 8/10 | Xcommunity | |
Migrate an existing project from the incumbent tool with documented import or conversion tooling G Migration | switcher | Migration adoption — stories about migration adoption in this arenaMigration adoption | 2 | full | 8/10 | Xcommunity | |
Trust that fetched packages are verified against checksums, signatures, or attestations before they run C Integrity | platform-engineer | Security supply chain — stories about security supply chain in this arenaSecurity supply chain | 2 | full | 8/10 | Cclaimed | |
Turn on protections against malicious packages, such as blocking lifecycle scripts or enforcing a minimum release age C Hardening | platform-engineer | Security supply chain — stories about security supply chain in this arenaSecurity supply chain | 2 | full | 8/10 | Cclaimed | |
Read the product's source under an open license G | ai-native user | Openness — open source, data portability, and self-hosting storiesOpenness | 2 | partial | 6/10 | Cclaimed | |
Add, remove, and upgrade dependencies through CLI commands that safely rewrite the manifest and lockfile, so an agent never hand-edits them C Manifest editing | ai-native user | Agent experience — stories about agent experience in this arenaAgent experience | 2 | partial | 5/10 | Cclaimed | |
Perform bulk operations across many items at once G | ai-native user | Automation depth — how much of the product can run unattendedAutomation depth | 2 | partial | 5/10 | Cclaimed | |
Use the same workflow and config on macOS, Linux, and Windows C Platform parity | developer | Cross platform — stories about cross platform in this arenaCross platform | 2 | partial | 5/10 | Xcommunity | |
Point the manager at private registries or mirrors with scoped authentication C Private registries | platform-engineer | Ecosystem extensibility — stories about ecosystem extensibility in this arenaEcosystem extensibility | 2 | partial | 4/10 | Cclaimed | |
Get machine-readable (JSON) output from core commands so an agent can parse results instead of scraping text G Structured output | ai-native user | Agent experience — stories about agent experience in this arenaAgent experience | 2 | partial | 3/10 | Cclaimed | |
Do everything through the API that I can do in the UI G | ai-native user | Openness — open source, data portability, and self-hosting storiesOpenness | 2 | n/a | 0/10 | ||
Enforce a frozen/immutable lockfile mode that fails the install when the manifest and lockfile disagree C Lockfiles | platform-engineer | Install reproducibility — stories about install reproducibility in this arenaInstall reproducibility | 2 | none | 0/10 | ||
Run installs and scripts filtered to a subset of workspace packages (including only those affected by a change) C Workspaces | developer | Monorepo workspaces — stories about monorepo workspaces in this arenaMonorepo workspaces | 2 | none | 0/10 | ||
Schedule recurring jobs or workflows G | ai-native user | Automation depth — how much of the product can run unattendedAutomation depth | 2 | none | 0/10 | ||
Choose where my data is stored (region/residency) G | ai-native user | Privacy posture — data-handling and privacy storiesPrivacy posture | 2 | n/a | untested | none yet | |
Control data retention and deletion G | ai-native user | Privacy posture — data-handling and privacy storiesPrivacy posture | 2 | none | untested | none yet | |
Opt out of telemetry and usage tracking G | ai-native user | Privacy posture — data-handling and privacy storiesPrivacy posture | 2 | none | untested | none yet | |
Rely on a shared content-addressable store so the same dependency version is stored once on disk across all projects C Disk efficiency | developer | Performance caching — stories about performance caching in this arenaPerformance caching | 2 | none | untested | none yet | |
Have the right tool versions and environment variables activate automatically when I enter a project directory C Environments | developer | Toolchain management — stories about toolchain management in this arenaToolchain management | 1 | full | 9/10 | Xcommunity | |
Extend the manager through third-party taps, overlays, plugins, or backends C Extensibility | developer | Ecosystem extensibility — stories about ecosystem extensibility in this arenaEcosystem extensibility | 1 | full | 8/10 | Xcommunity | |
Point an agent at a documented, text-based lockfile format it can read and diff C Structured output | ai-native user | Agent experience — stories about agent experience in this arenaAgent experience | 1 | partial | 5/10 | Cclaimed | |
Version, review, and roll back my automations G | ai-native user | Automation depth — how much of the product can run unattendedAutomation depth | 1 | partial | 4/10 | Cclaimed | |
See published benchmarks or measured numbers backing the manager's speed claims C Benchmarks | developer | Performance caching — stories about performance caching in this arenaPerformance caching | 1 | none | 0/10 |
Opportunities — the stories that would move this product's scores, from its own judged verdictsOpportunitiestop 8 of 28 stories with headroom
What would move mise’s scores — derived from its own judged verdicts, biggest headroom first. Each line quotes what the judge found missing; shipping it (or evidencing it publicly) is the fix.
Security supply chain — stories about security supply chain in this arenaAudit installed dependencies for known vulnerabilities directly from the CLI
nonemoves PA Scoreimpact 30
Evidence shows mise verifies signatures/provenance (Cosign, SLSA, GitHub attestations) and supports minimum release age restrictions, but there is no documented CLI command or feature for scanning installed tool/dependency versions against known CVE databases (no 'mise audit' or vulnerability report capability found).
Agenticness — how well agents can access and operate the productOperate the product with natural-language commands
nonemoves Built-in AIimpact 30
All evidence shows mise operates via explicit CLI subcommands and TOML config (mise use, mise exec, mise run, etc.) with no natural-language command interface documented anywhere, including in the llms.txt probe which is just an AI-readable docs index, not an NL command layer.
Agenticness — how well agents can access and operate the productExplore an interactive API reference with runnable examples
nonemoves API qualityimpact 30
No evidence of an interactive API reference with runnable examples; probes explicitly show no OpenAPI/swagger spec and no runnable docs page (404s), only static CLI documentation and an llms.txt for LLM consumption.
Agenticness — how well agents can access and operate the productDownload a machine-readable API spec (OpenAPI or equivalent)
nonemoves API qualityimpact 30
mise is a CLI tool, not an API-based service, but the story explicitly asks about a machine-readable API spec, and the evidence pack directly probes for this and finds no OpenAPI/swagger endpoint (all 404).
Agenticness — how well agents can access and operate the productRely on versioned APIs with a documented deprecation policy
nonemoves API qualityimpact 30
mise is a CLI/tool manager and no evidence in the pack shows a versioned API with a documented deprecation policy; the openapi probe returned 404s for all candidate API spec paths, and no docs discuss API versioning or deprecation guarantees.
Automation depth — how much of the product can run unattendedSchedule recurring jobs or workflows
nonemoves PA Scoreimpact 20
mise provides task running (mise run), file-triggered rebuilds (mise watch), and CI integration, but there is no evidence of any built-in scheduler, cron-like recurring job trigger, or workflow scheduling feature — tasks only run on-demand or via file-change/CI triggers.
Performance caching — stories about performance caching in this arenaRely on a shared content-addressable store so the same dependency version is stored once on disk across all projects
nonemoves PA Scoreimpact 20
Missing: explicit documentation of install directory structure, content-addressing/hashing scheme, and disk-space dedup guarantees across projects.
Install reproducibility — stories about install reproducibility in this arenaEnforce a frozen/immutable lockfile mode that fails the install when the manifest and lockfile disagree
nonemoves PA Scoreimpact 20
The evidence pack shows mise has lockfile-related features (e.g.
Showing the top 8 of 28 — every none/partial verdict in the story verdicts table is headroom.
Think a verdict is wrong? Every verdicts-table row has a Flag link — see the methodology.
Coverage map — which docs area, API section, or community source covers which judged storiesCoverage map14 surfaces · 29 covered stories
Where the cited evidence behind each covered verdict came from — the same citations the verdicts table shows, no extra judging.
mise.jdx.dev16 stories
- Get machine-readable (JSON) output from core commands so an agent can parse results instead of scraping text
- Point an agent at a documented, text-based lockfile format it can read and diff
- Perform bulk operations across many items at once
- Define rules that trigger actions automatically on events
- Version, review, and roll back my automations
- Use the same workflow and config on macOS, Linux, and Windows
- Extend the manager through third-party taps, overlays, plugins, or backends
- Install almost anything I need from a large, actively maintained package registry or repository
- Bootstrap a fresh clone with one command that installs everything the project declares
- Install dependencies from a lockfile and get the exact same resolved versions on every machine
- Pin exact versions of packages and tools per project and have the manager respect those pins
- Keep using familiar commands and interface conventions from the incumbent tool while adopting this manager
- Migrate an existing project from the incumbent tool with documented import or conversion tooling
- Export all of my data in open formats and leave
- Have the right tool versions and environment variables activate automatically when I enter a project directory
- Install and switch language runtimes or tool versions per project from a checked-in config file
Hacker News13 stories
- Run the product headlessly / in CI for automation
- Use an official CLI
- Use the same workflow and config on macOS, Linux, and Windows
- Extend the manager through third-party taps, overlays, plugins, or backends
- Install almost anything I need from a large, actively maintained package registry or repository
- Bootstrap a fresh clone with one command that installs everything the project declares
- Pin exact versions of packages and tools per project and have the manager respect those pins
- Keep using familiar commands and interface conventions from the incumbent tool while adopting this manager
- Migrate an existing project from the incumbent tool with documented import or conversion tooling
- Install prebuilt binary packages from a cache instead of compiling from source
- Make CI installs fast with a documented cache-restore setup and offline-capable installs
- Have the right tool versions and environment variables activate automatically when I enter a project directory
- Install and switch language runtimes or tool versions per project from a checked-in config file
Dev tools docs12 stories
- Define rules that trigger actions automatically on events
- Use the same workflow and config on macOS, Linux, and Windows
- Extend the manager through third-party taps, overlays, plugins, or backends
- Point the manager at private registries or mirrors with scoped authentication
- Install almost anything I need from a large, actively maintained package registry or repository
- Pin exact versions of packages and tools per project and have the manager respect those pins
- Keep using familiar commands and interface conventions from the incumbent tool while adopting this manager
- Migrate an existing project from the incumbent tool with documented import or conversion tooling
- Export all of my data in open formats and leave
- Trust that fetched packages are verified against checksums, signatures, or attestations before they run
- Have the right tool versions and environment variables activate automatically when I enter a project directory
- Install and switch language runtimes or tool versions per project from a checked-in config file
Getting started docs9 stories
- Have an agent install and update project dependencies non-interactively, with clear exit codes and errors when something fails
- Add, remove, and upgrade dependencies through CLI commands that safely rewrite the manifest and lockfile, so an agent never hand-edits them
- Use an official CLI
- Drive the product through a documented public API
- Use the same workflow and config on macOS, Linux, and Windows
- Install almost anything I need from a large, actively maintained package registry or repository
- Pin exact versions of packages and tools per project and have the manager respect those pins
- Have the right tool versions and environment variables activate automatically when I enter a project directory
- Install and switch language runtimes or tool versions per project from a checked-in config file
Security docs9 stories
- Add, remove, and upgrade dependencies through CLI commands that safely rewrite the manifest and lockfile, so an agent never hand-edits them
- Get machine-readable (JSON) output from core commands so an agent can parse results instead of scraping text
- Point an agent at a documented, text-based lockfile format it can read and diff
- Drive the product through a documented public API
- Install dependencies from a lockfile and get the exact same resolved versions on every machine
- Install prebuilt binary packages from a cache instead of compiling from source
- Make CI installs fast with a documented cache-restore setup and offline-capable installs
- Turn on protections against malicious packages, such as blocking lifecycle scripts or enforcing a minimum release age
- Trust that fetched packages are verified against checksums, signatures, or attestations before they run
Configuration docs8 stories
- Add, remove, and upgrade dependencies through CLI commands that safely rewrite the manifest and lockfile, so an agent never hand-edits them
- Point an agent at a documented, text-based lockfile format it can read and diff
- Version, review, and roll back my automations
- Use the same workflow and config on macOS, Linux, and Windows
- Install dependencies from a lockfile and get the exact same resolved versions on every machine
- Export all of my data in open formats and leave
- Have the right tool versions and environment variables activate automatically when I enter a project directory
- Install and switch language runtimes or tool versions per project from a checked-in config file
Continuous integration docs8 stories
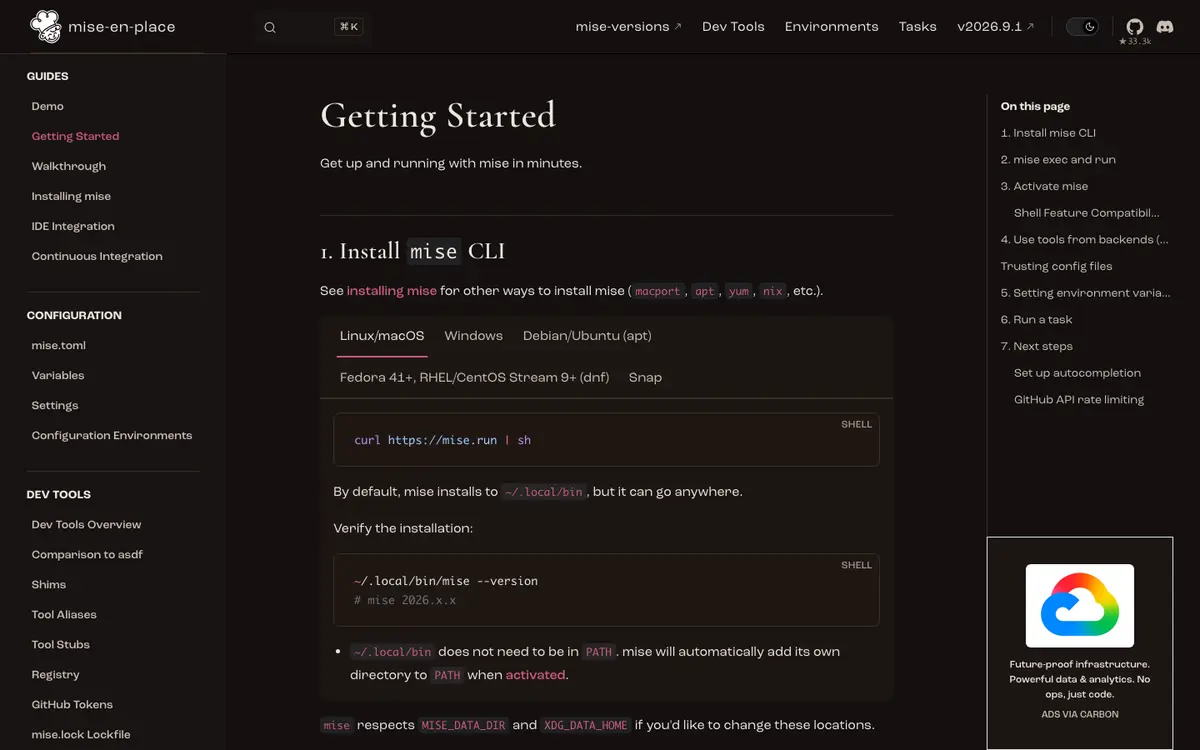
- Have an agent install and update project dependencies non-interactively, with clear exit codes and errors when something fails
- Run the product headlessly / in CI for automation
- Bootstrap a fresh clone with one command that installs everything the project declares
- Install dependencies from a lockfile and get the exact same resolved versions on every machine
- Pin exact versions of packages and tools per project and have the manager respect those pins
- Read the product's source under an open license
- Make CI installs fast with a documented cache-restore setup and offline-capable installs
- Turn on protections against malicious packages, such as blocking lifecycle scripts or enforcing a minimum release age
Registry docs4 stories
- Extend the manager through third-party taps, overlays, plugins, or backends
- Point the manager at private registries or mirrors with scoped authentication
- Install almost anything I need from a large, actively maintained package registry or repository
- Install prebuilt binary packages from a cache instead of compiling from source
Tasks docs4 stories
llms.txt3 stories
GitHub README3 stories
Probe proofs — replayable recordings from the probe harnessProbe proofs
Replayable recordings from our probe harness — see the Prove-It protocol to submit one.
$mise --versionreproduced$ mise --version
_ __
____ ___ (_)_______ ___ ____ ____ / /___ _________
/ __ `__ \/ / ___/ _ \______/ _ \/ __ \______/ __ \/ / __ `/ ___/ _ \
/ / / / / / (__ ) __/_____/ __/ / / /_____/ /_/ / / /_/ / /__/ __/
/_/ /_/ /_/_/____/\___/ \___/_/ /_/ / .___/_/\__,_/\___/\___/
/_/ by @jdx
2026.7.2 macos-arm64 (2026-07-07)
mise WARN mise version 2026.9.1 available
$mise ls --json && mise registry | head -12reproduced$ mise ls --json && mise registry | head -12
{
"actionlint": [
{
"version": "1.7.12",
"install_path": "/Users/judegomila/.local/share/mise/installs/actionlint/1.7.12",
"installed": true,
"active": false
}
],
"aqua:sqlc-dev/sqlc": [
{
"version": "1.31.1",
"install_path": "/Users/judegomila/.local/share/mise/installs/aqua-sqlc-dev-sqlc/1.31.1",
"installed": true,
"active": false
}
],
"ast-grep": [
{
"version": "0.44.1",
"install_path": "/Users/judegomila/.local/share/mise/installs/ast-grep/0.44.1",
"installed": true,
"active": false
}
],
"aws": [
{
"version": "2.35.17",
"install_path": "/Users/judegomila/.local/share/mise/installs/aws/2.35.17",
"installed": true,
"active": false
}
],
"aws-cli": [
{
"version": "2.35.17",
"install_path": "/Users/judegomila/.local/share/mise/installs/aws-cli/2.35.17",
"installed": true,
"active": false
}
],
"bat": [
{
"version": "0.26.1",
"install_path": "/Users/judegomila/.local/share/mise/installs/bat/0.26.1",
"installed": true,
"active": false
}
],
"bats": [
{
"version": "1.13.0",
"install_path": "/Users/judegomila/.local/share/mise/installs/bats/1.13.0",
"installed": true,
"active": false
}
],
"coder": [
{
"version": "2.33.6",
"install_path": "/Users/judegomila/.local/share/mise/installs/coder/2.33.6",
"installed": true,
"active": false
},
{
"version": "2.34.5",
"install_path": "/Users/judegomila/.local/share/mise/installs/coder/2.34.5",
"installed": true,
"active": false
}
],
"eza": [
{
"version": "0.23.4",
"install_path": "/Users/judegomila/.local/share/mise/installs/eza/0.23.4",
"installed": true,
"active": false
}
],
"fd": [
{
"version": "10.4.2",
"install_path": "/Users/judegomila/.local/share/mise/installs/fd/10.4.2",
"installed": true,
"active": false
}
],
"fzf": [
{
"version": "0.73.1",
"install_path": "/Users/judegomila/.local/share/mise/installs/fzf/0.73.1",
"installed": true,
"active": false
}
],
"gh": [
{
"version": "2.95.0",
"install_path": "/Users/judegomila/.local/share/mise/installs/gh/2.95.0",
"installed": true,
"active": false
},
{
"version": "2.96.0",
"install_path": "/Users/judegomila/.local/share/mise/installs/gh/2.96.0",
"installed": true,
"active": false
}
],
"helm": [
{
"version": "4.2.2",
"install_path": "/Users/judegomila/.local/share/mise/installs/helm/4.2.2",
"installed": true,
"active": false
}
],
"jq": [
{
"version": "1.8.2",
"install_path": "/Users/judegomila/.local/share/mise/installs/jq/1.8.2",
"installed": true,
"active": false
}
],
"jsonschema": [
{
"version": "16.0.0",
"install_path": "/Users/judegomila/.local/share/mise/installs/jsonschema/16.0.0",
"installed": true,
"active": false
}
],
"kubectl": [
{
"version": "1.36.2",
"install_path": "/Users/judegomila/.local/share/mise/installs/kubectl/1.36.2",
"installed": true,
"active": false
}
],
"mkcert": [
{
"version": "1.4.4",
"install_path": "/Users/judegomila/.local/share/mise/installs/mkcert/1.4.4",
"installed": true,
"active": false
}
],
"node": [
{
"version": "24.18.0",
"install_path": "/Users/judegomila/.local/share/mise/installs/node/24.18.0",
"installed": true,
"active": false
},
{
"version": "25.9.0",
"install_path": "/Users/judegomila/.local/share/mise/installs/node/25.9.0",
"installed": true,
"active": false
}
],
"npm:@dotenvx/dotenvx": [
{
"version": "~1.75.0",
"install_path": "/Users/judegomila/.local/share/mise/installs/npm-dotenvx-dotenvx/~1.75.0",
"installed": true,
"active": false
},
{
"version": "~2.1.0",
"install_path": "/Users/judegomila/.local/share/mise/installs/npm-dotenvx-dotenvx/~2.1.0",
"installed": true,
"active": false
}
],
"npm:@taplo/cli": [
{
"version": "0.7.0",
"install_path": "/Users/judegomila/.local/share/mise/installs/npm-taplo-cli/0.7.0",
"installed": true,
"active": false
}
],
"npm:graphile-migrate": [
{
"version": "2.0.0-rc.3",
"install_path": "/Users/judegomila/.local/share/mise/installs/npm-graphile-migrate/2.0.0-rc.3",
"installed": true,
"active": false
}
],
"oxipng": [
{
"version": "10.1.1",
"install_path": "/Users/judegomila/.local/share/mise/installs/oxipng/10.1.1",
"installed": true,
"active": false
}
],
"python": [
{
"version": "3.11.15",
"install_path": "/Users/judegomila/.local/share/mise/installs/python/3.11.15",
"installed": true,
"active": false
},
{
"version": "3.14.3",
"install_path": "/Users/judegomila/.local/share/mise/installs/python/3.14.3",
"installed": true,
"active": false
},
{
"version": "3.14.6",
"install_path": "/Users/judegomila/.local/share/mise/installs/python/3.14.6",
"installed": true,
"active": false
},
{
"version": "3.14.7",
"install_path": "/Users/judegomila/.local/share/mise/installs/python/3.14.7",
"installed": true,
"active": false
}
],
"ripgrep": [
{
"version": "15.1.0",
"install_path": "/Users/judegomila/.local/share/mise/installs/ripgrep/15.1.0",
"installed": true,
"active": false
}
],
"shellcheck": [
{
"version": "0.11.0",
"install_path": "/Users/judegomila/.local/share/mise/installs/shellcheck/0.11.0",
"installed": true,
"active": false
}
],
"stripe": [
{
"version": "1.43.6",
"install_path": "/Users/judegomila/.local/share/mise/installs/stripe/1.43.6",
"installed": true,
"active": false
}
],
"terraform": [
{
"version": "1.15.7",
"install_path": "/Users/judegomila/.local/share/mise/installs/terraform/1.15.7",
"installed": true,
"active": false
}
],
"ubi:ory/cli": [
{
"version": "1.3.0",
"install_path": "/Users/judegomila/.local/share/mise/installs/ubi-ory-cli/1.3.0",
"installed": true,
"active": false
}
],
"uv": [
{
"version": "0.9.30",
"install_path": "/Users/judegomila/.local/share/mise/installs/uv/0.9.30",
"installed": true,
"active": false
},
{
"version": "0.11.24",
"install_path": "/Users/judegomila/.local/share/mise/installs/uv/0.11.24",
"installed": true,
"active": false
},
{
"version": "0.11.26",
"install_path": "/Users/judegomila/.local/share/mise/installs/uv/0.11.26",
"installed": true,
"active": false
},
{
"version": "0.12.1",
"install_path": "/Users/judegomila/.local/share/mise/installs/uv/0.12.1",
"installed": true,
"active": false
},
{
"version": "0.12.3",
"install_path": "/Users/judegomila/.local/share/mise/installs/uv/0.12.3",
"installed": true,
"active": false
}
],
"watchexec": [
{
"version": "2.5.1",
"install_path": "/Users/judegomila/.local/share/mise/installs/watchexec/2.5.1",
"installed": true,
"active": false
}
],
"zellij": [
{
"version": "0.44.3",
"install_path": "/Users/judegomila/.local/share/mise/installs/zellij/0.44.3",
"installed": true,
"active": false
}
]
}
1password vfox:mise-plugins/vfox-1password aqua:1password/cli
1password-cli vfox:mise-plugins/vfox-1password aqua:1password/cli
aapt2 vfox:mise-plugins/vfox-aapt2
acli aqua:atlassian.com/acli
act aqua:nektos/act asdf:gr1m0h/asdf-act
action-validator aqua:mpalmer/action-validator asdf:mpalmer/action-validator cargo:action-validator
actionlint aqua:rhysd/actionlint asdf:crazy-matt/asdf-actionlint go:github.com/rhysd/actionlint/cmd/actionlint
adr-tools aqua:npryce/adr-tools asdf:https://gitlab.com/td7x/asdf/adr-tools
ag vfox:mise-plugins/vfox-ag asdf:mise-plugins/mise-ag
age aqua:FiloSottile/age asdf:threkk/asdf-age
age-plugin-yubi[redacted] github:str4d/age-plugin-yubi[redacted] asdf:joke/asdf-age-plugin-yubi[redacted] cargo:age-plugin-yubi[redacted]
agebox aqua:slok/agebox asdf:slok/asdf-agebox
Claims vs evidence — vendor claims reconciled against independent verdictsClaims vs evidence
9 of 13 testable claims verified · 0 contradicted → integrity 69/100
38 distinct capability claims found in mise’s own claimed-docs/GitHub materials, reconciled against our judge’s independent verdicts.
9
Verified
4
Unverified
0
Contradicted
16
Undersold
Verified (25)
“Run any tool at a specific version instantly via mise exec/x without a permanent install”
Install and switch language runtimes or tool versions per project from a checked-in config filefullproof ↗
“Install a tool and set it as the global default version with one command”
Install and switch language runtimes or tool versions per project from a checked-in config filefullproof ↗
“Reads and is compatible with asdf .tool-versions files and idiomatic version files like .node-version”
Keep using familiar commands and interface conventions from the incumbent tool while adopting this managerfullproof ↗
“Reads and is compatible with asdf .tool-versions files and idiomatic version files like .node-version”
Migrate an existing project from the incumbent tool with documented import or conversion toolingfullproof ↗
“Install and run a tool directly from a GitHub repo/release”
Install almost anything I need from a large, actively maintained package registry or repositoryfullproof ↗
“Automatically switches active tool versions as you move between project directories”
Have the right tool versions and environment variables activate automatically when I enter a project directoryfullproof ↗
“mise bootstrap provisions a fresh machine: OS packages, dotfiles, repos, macOS defaults, and services”
Bootstrap a fresh clone with one command that installs everything the project declaresfullproof ↗
“Loads per-project environment variables from mise.toml, .env files, and secrets, active only while in the project”
Have the right tool versions and environment variables activate automatically when I enter a project directoryfullproof ↗
“Backend used to install a tool can be overridden via MISE_BACKENDS_<TOOL> environment variables”
Extend the manager through third-party taps, overlays, plugins, or backendsfullproof ↗
“Provides an official mise-action for CI that installs mise and configured tools”
Run the product headlessly / in CI for automationfullproof ↗
“Config files are looked up hierarchically in parent directories and merged, with closer files taking precedence”
Have the right tool versions and environment variables activate automatically when I enter a project directoryfullproof ↗
“A single checked-in config file replaces scattered dotfiles, so setup is just git clone + mise bootstrap”
Bootstrap a fresh clone with one command that installs everything the project declaresfullproof ↗
“Missing tool versions are automatically downloaded and installed on first use”
Install and switch language runtimes or tool versions per project from a checked-in config filefullproof ↗
“Shell activation (eval mise activate) sets up automatic PATH/env management”
Have the right tool versions and environment variables activate automatically when I enter a project directoryfullproof ↗
“Can install packages globally from npm registry (e.g. mise use --global npm:pkg)”
Install almost anything I need from a large, actively maintained package registry or repositoryfullproof ↗
“Supports a shims mode that creates shims instead of modifying PATH”
Have the right tool versions and environment variables activate automatically when I enter a project directoryfullproof ↗
“Provides an official install script (curl mise.run) to bootstrap the mise CLI itself”
Bootstrap a fresh clone with one command that installs everything the project declaresfullproof ↗
“Ships its own Homebrew implementation, installing formulae and casks without requiring Homebrew itself”
Install almost anything I need from a large, actively maintained package registry or repositoryfullproof ↗
“Can install Python packages from PyPI via pipx as a backend”
Install almost anything I need from a large, actively maintained package registry or repositoryfullproof ↗
“Specific backends (e.g. asdf) can be disabled via settings”
Extend the manager through third-party taps, overlays, plugins, or backendsfullproof ↗
“Can install tools from many different registries in one config: npm, PyPI, GitHub releases, etc.”
Install almost anything I need from a large, actively maintained package registry or repositoryfullproof ↗
“GitHub and aqua backends give access to almost all programs published on GitHub”
Install almost anything I need from a large, actively maintained package registry or repositoryfullproof ↗
“Recommends and supports pinning tools to exact versions for reproducible environments”
Pin exact versions of packages and tools per project and have the manager respect those pinsfullproof ↗
“mise ls --current lists active tool versions and their config source for the current directory”
Install and switch language runtimes or tool versions per project from a checked-in config filefullproof ↗
“Can set environment variables directly via CLI (mise set VAR=value)”
Have the right tool versions and environment variables activate automatically when I enter a project directoryfullproof ↗
Unverified (7)
“MISE_SAFE=1 mode prevents project configuration from executing arbitrary code”
Turn on protections against malicious packages, such as blocking lifecycle scripts or enforcing a minimum release agefullproof ↗
“Can restrict installs to tool versions released before a certain date or minimum age”
Turn on protections against malicious packages, such as blocking lifecycle scripts or enforcing a minimum release agefullproof ↗
“Automatically verifies Cosign/Minisign signatures, SLSA provenance, and GitHub attestations for aqua-backend tools”
Trust that fetched packages are verified against checksums, signatures, or attestations before they runfullproof ↗
“Prompts the user to trust untrusted project config files before executing them”
Turn on protections against malicious packages, such as blocking lifecycle scripts or enforcing a minimum release agefullproof ↗
“Supports custom HTTP-backend tool definitions with per-platform URLs and checksums”
Trust that fetched packages are verified against checksums, signatures, or attestations before they runfullproof ↗
“mise lock command supports --bump/--dry-run with JSON output for updating the lockfile”
Get machine-readable (JSON) output from core commands so an agent can parse results instead of scraping textpartialproof ↗
“mise lock command supports --bump/--dry-run with JSON output for updating the lockfile”
Point an agent at a documented, text-based lockfile format it can read and diffpartialproof ↗
Undersold (16)
Have an agent install and update project dependencies non-interactively, with clear exit codes and errors when something failspartialproof ↗
Add, remove, and upgrade dependencies through CLI commands that safely rewrite the manifest and lockfile, so an agent never hand-edits thempartialproof ↗
Point an agent at llms.txt or agent-oriented docsfullproof ↗
Drive the product through a documented public APIpartialproof ↗
Set up automations that run autonomously in the backgroundpartialproof ↗
Perform bulk operations across many items at oncepartialproof ↗
Define rules that trigger actions automatically on eventspartialproof ↗
Use the same workflow and config on macOS, Linux, and Windowspartialproof ↗
Point the manager at private registries or mirrors with scoped authenticationpartialproof ↗
Install dependencies from a lockfile and get the exact same resolved versions on every machinepartialproof ↗
Export all of my data in open formats and leavepartialproof ↗
Read the product's source under an open licensepartialproof ↗
Install prebuilt binary packages from a cache instead of compiling from sourcepartialproof ↗
Make CI installs fast with a documented cache-restore setup and offline-capable installspartialproof ↗
Claims outside our story set (8)
Real capability claims found in mise’s own materials, but no story in this arena’s taxonomy covers them yet — that’s feedback on the taxonomy, not a mark against the product.
“Define and run project tasks for building, testing, linting, and deploying”
source ↗“mise watch automatically rebuilds/reruns tasks on file changes”
source ↗“Tasks can be written as standalone executable bash scripts instead of embedded in yml/json/toml strings”
source ↗“Task/dependency builds run in parallel by default with no extra configuration”
source ↗“Manages dotfiles as symlinks, copies, or templates with single-line edits”
source ↗“Can bootstrap remote hosts over SSH via mise bootstrap remote”
source ↗“Run a defined task by name, e.g. mise run build”
source ↗“Tasks can declare dependencies on other tasks (depends = [...])”
source ↗
Business model
Free, MIT-licensed polyglot tool-version manager, env manager, and task runner maintained by Jeff Dickey (jdx) and contributors; funded via GitHub Sponsors.
pricing ↗Score trend
How this product’s scores have moved as evidence and verdicts are re-derived — a point per change, not per day.
Try Experimental
Run it in the microterminal →Recorded agent sessions — and a live MCP handshake where the vendor ships one.
Flag
⚑ Flag a verdictThink a verdict is wrong? Opens a prefilled GitHub issue — or use the ⚑ next to any verdict above.
For agents
Agent surface uptime llms.txt 100% (30d, checked every 6h since Sep 8 '26)