Rank #4 of 6 in Package & Toolchain Managers
Access
Install
 vs Homebrew
 vs Nix
 vs pnpm
 vs Bun (package manager)
 vs mise
Showcase
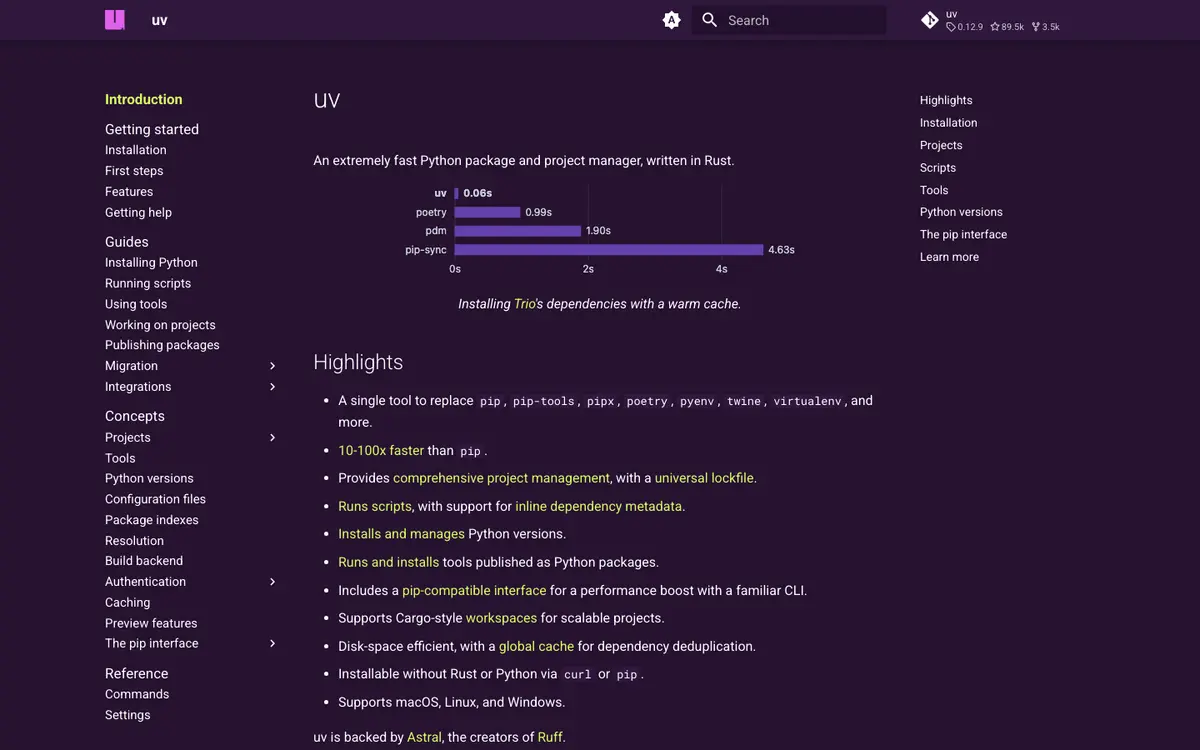
Try itExperimental
See what an agent can do with uv before you ever sign up. Pick a story: recorded sessions replay real probe-harness transcripts; sandboxed self-drive sessions are designed and gated (docs/TRY-IT.md).
$uv --versionrecorded session — replayed, not liveVerified integrations
Connections to other tracked products — hover a chip for the verbatim evidence quote behind it.

By theme — the product's score on each story themeBy theme
Agent experience — stories about agent experience in this arenaAgent experienceevidence →
Stories about agent experience in this arena
Agenticness — how well agents can access and operate the productAgenticnessevidence →
How well agents can access and operate the product
Automation depth — how much of the product can run unattendedAutomation depthevidence →
How much of the product can run unattended
Cross platform — stories about cross platform in this arenaCross platformevidence →
Stories about cross platform in this arena
Ecosystem extensibility — stories about ecosystem extensibility in this arenaEcosystem extensibilityevidence →
Stories about ecosystem extensibility in this arena
Install reproducibility — stories about install reproducibility in this arenaInstall reproducibilityevidence →
Stories about install reproducibility in this arena
Migration adoption — stories about migration adoption in this arenaMigration adoptionevidence →
Stories about migration adoption in this arena
Monorepo workspaces — stories about monorepo workspaces in this arenaMonorepo workspacesevidence →
Stories about monorepo workspaces in this arena
Openness — open source, data portability, and self-hosting storiesOpennessevidence →
Open source, data portability, and self-hosting stories
Performance caching — stories about performance caching in this arenaPerformance cachingevidence →
Stories about performance caching in this arena
Privacy posture — data-handling and privacy storiesPrivacy postureevidence →
Data-handling and privacy stories
Security supply chain — stories about security supply chain in this arenaSecurity supply chainevidence →
Stories about security supply chain in this arena
Toolchain management — stories about toolchain management in this arenaToolchain managementevidence →
Stories about toolchain management in this arena
Story verdicts — every judged story with its evidenceStory verdicts
Follow the green: where the map greys out is where uv stops today. ✓ full · ~ partial · ! disputed · — none · n/a not applicable.
Agent experience — stories about agent experience in this arenaAgent experience
Stories about agent experience in this arena
Agenticness — how well agents can access and operate the productAgenticness
How well agents can access and operate the product
API surface
Drive the product through a documented public API
~5/10
unlocks → Official SDKs · Versioning policy · Extend the manager through third-party taps, overlays, plugins, or backends · Point the manager at private registries or mirrors with scoped authentication
Subscribe to events via webhooks
n/an/a
Build against official SDKs
—–
Issue scoped/least-privilege API credentials for an agent
n/an/a
Connect an agent via an official MCP server
n/an/a
Download a machine-readable API spec (OpenAPI or equivalent)
~4/10
unlocks → Interactive API docs · Official SDKs
Rely on versioned APIs with a documented deprecation policy
—0/10
Test against a sandbox environment without touching production data
n/an/a
Explore an interactive API reference with runnable examples
—0/10
Docs for agents
Point an agent at llms.txt or agent-oriented docs
✓8/10
Agentic features
Delegate tasks to a built-in AI assistant inside the product
n/an/a
Operate the product with natural-language commands
—–
Plug MCP servers into this product so it can use their tools
n/an/a
Get AI-generated insights and suggestions from my data inside the product
n/an/a
Set up automations that run autonomously in the background
n/an/a
Automation depth — how much of the product can run unattendedAutomation depth
How much of the product can run unattended
Cross platform — stories about cross platform in this arenaCross platform
Stories about cross platform in this arena
Ecosystem extensibility — stories about ecosystem extensibility in this arenaEcosystem extensibility
Stories about ecosystem extensibility in this arena
Install reproducibility — stories about install reproducibility in this arenaInstall reproducibility
Stories about install reproducibility in this arena
Migration adoption — stories about migration adoption in this arenaMigration adoption
Stories about migration adoption in this arena
Monorepo workspaces — stories about monorepo workspaces in this arenaMonorepo workspaces
Stories about monorepo workspaces in this arena
Openness — open source, data portability, and self-hosting storiesOpenness
Open source, data portability, and self-hosting stories
Performance caching — stories about performance caching in this arenaPerformance caching
Stories about performance caching in this arena
See published benchmarks or measured numbers backing the manager's speed claims
—0/10
Install prebuilt binary packages from a cache instead of compiling from source
✓8/10
Make CI installs fast with a documented cache-restore setup and offline-capable installs
~7/10
Rely on a shared content-addressable store so the same dependency version is stored once on disk across all projects
✓8/10
Privacy posture — data-handling and privacy storiesPrivacy posture
Data-handling and privacy stories
Security supply chain — stories about security supply chain in this arenaSecurity supply chain
Stories about security supply chain in this arena
Audit installed dependencies for known vulnerabilities directly from the CLI
—–
Turn on protections against malicious packages, such as blocking lifecycle scripts or enforcing a minimum release age
—–
Trust that fetched packages are verified against checksums, signatures, or attestations before they run
—–
Toolchain management — stories about toolchain management in this arenaToolchain management
Stories about toolchain management in this arena
Sorted by importance (agentic first) (high → low) · 54/54 stories · click a row’s chevron for the rationale and evidence
Drive the product through a documented public API G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 3 | partial | 5/10 | Tprobed | |
Connect an agent via an official MCP server G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 3 | n/a | untested | none yet | |
Delegate tasks to a built-in AI assistant inside the product G Agentic features | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 3 | n/a | untested | none yet | |
Plug MCP servers into this product so it can use their tools G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 3 | n/a | untested | none yet | |
Use an official CLI G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | full | 9/10 | Tprobed | |
Point an agent at llms.txt or agent-oriented docs G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | full | 8/10 | Tprobed | |
Run the product headlessly / in CI for automation G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | full | 8/10 | Xcommunity | |
Download a machine-readable API spec (OpenAPI or equivalent) G Api quality | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | partial | 4/10 | Tprobed | |
Explore an interactive API reference with runnable examples G Api quality | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | none | 0/10 | ||
Rely on versioned APIs with a documented deprecation policy G Api quality | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | none | 0/10 | ||
Build against official SDKs G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | none | untested | none yet | |
Get AI-generated insights and suggestions from my data inside the product G Agentic features | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | n/a | untested | none yet | |
Issue scoped/least-privilege API credentials for an agent G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | n/a | untested | none yet | |
Operate the product with natural-language commands G Agentic features | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | none | untested | none yet | |
Set up automations that run autonomously in the background G Agentic features | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | n/a | untested | none yet | |
Subscribe to events via webhooks G Agent access | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 2 | n/a | untested | none yet | |
Test against a sandbox environment without touching production data G Api quality | ai-native user | Agenticness — how well agents can access and operate the productAgenticness | 1 | n/a | untested | none yet | |
Pin exact versions of packages and tools per project and have the manager respect those pins C Pinning | developer | Install reproducibility — stories about install reproducibility in this arenaInstall reproducibility | 3 | full | 9/10 | Xcommunity | |
Install prebuilt binary packages from a cache instead of compiling from source C Binary caching | developer | Performance caching — stories about performance caching in this arenaPerformance caching | 3 | full | 8/10 | Xcommunity | |
Install dependencies from a lockfile and get the exact same resolved versions on every machine C Lockfiles | developer | Install reproducibility — stories about install reproducibility in this arenaInstall reproducibility | 3 | full | 7/10 | Cclaimed | |
Make CI installs fast with a documented cache-restore setup and offline-capable installs C Ci speed | platform-engineer | Performance caching — stories about performance caching in this arenaPerformance caching | 3 | partial | 7/10 | Xcommunity | |
Manage many packages in one monorepo with workspaces sharing a single lockfile and cross-linked local dependencies C Workspaces | developer | Monorepo workspaces — stories about monorepo workspaces in this arenaMonorepo workspaces | 3 | full | 7/10 | Cclaimed | |
Have an agent install and update project dependencies non-interactively, with clear exit codes and errors when something fails C Headless installs | ai-native user | Agent experience — stories about agent experience in this arenaAgent experience | 3 | partial | 6/10 | Xcommunity | |
Export all of my data in open formats and leave G | ai-native user | Openness — open source, data portability, and self-hosting storiesOpenness | 3 | partial | 5/10 | Cclaimed | |
Audit installed dependencies for known vulnerabilities directly from the CLI C Auditing | platform-engineer | Security supply chain — stories about security supply chain in this arenaSecurity supply chain | 3 | none | untested | none yet | |
Define rules that trigger actions automatically on events G | ai-native user | Automation depth — how much of the product can run unattendedAutomation depth | 3 | n/a | untested | none yet | |
Prevent my data from being used to train AI models G | ai-native user | Privacy posture — data-handling and privacy storiesPrivacy posture | 3 | n/a | untested | none yet | |
Self-host the core product G | ai-native user | Openness — open source, data portability, and self-hosting storiesOpenness | 3 | n/a | untested | none yet | |
Add, remove, and upgrade dependencies through CLI commands that safely rewrite the manifest and lockfile, so an agent never hand-edits them C Manifest editing | ai-native user | Agent experience — stories about agent experience in this arenaAgent experience | 2 | full | 8/10 | Xcommunity | |
Bootstrap a fresh clone with one command that installs everything the project declares C Bootstrap | developer | Install reproducibility — stories about install reproducibility in this arenaInstall reproducibility | 2 | full | 8/10 | Xcommunity | |
Install almost anything I need from a large, actively maintained package registry or repository C Registry | developer | Ecosystem extensibility — stories about ecosystem extensibility in this arenaEcosystem extensibility | 2 | full | 8/10 | Xcommunity | |
Install and switch language runtimes or tool versions per project from a checked-in config file C Runtimes | developer | Toolchain management — stories about toolchain management in this arenaToolchain management | 2 | full | 8/10 | Cclaimed | |
Rely on a shared content-addressable store so the same dependency version is stored once on disk across all projects C Disk efficiency | developer | Performance caching — stories about performance caching in this arenaPerformance caching | 2 | full | 8/10 | Xcommunity | |
Keep using familiar commands and interface conventions from the incumbent tool while adopting this manager C Compatibility | switcher | Migration adoption — stories about migration adoption in this arenaMigration adoption | 2 | partial | 7/10 | Xcommunity | |
Use the same workflow and config on macOS, Linux, and Windows C Platform parity | developer | Cross platform — stories about cross platform in this arenaCross platform | 2 | full | 7/10 | Xcommunity | |
Migrate an existing project from the incumbent tool with documented import or conversion tooling G Migration | switcher | Migration adoption — stories about migration adoption in this arenaMigration adoption | 2 | partial | 6/10 | Xcommunity | |
Read the product's source under an open license G | ai-native user | Openness — open source, data portability, and self-hosting storiesOpenness | 2 | partial | 5/10 | Cclaimed | |
Get machine-readable (JSON) output from core commands so an agent can parse results instead of scraping text G Structured output | ai-native user | Agent experience — stories about agent experience in this arenaAgent experience | 2 | partial | 4/10 | Cclaimed | |
Perform bulk operations across many items at once G | ai-native user | Automation depth — how much of the product can run unattendedAutomation depth | 2 | partial | 4/10 | Cclaimed | |
Enforce a frozen/immutable lockfile mode that fails the install when the manifest and lockfile disagree C Lockfiles | platform-engineer | Install reproducibility — stories about install reproducibility in this arenaInstall reproducibility | 2 | none | 0/10 | ||
Run installs and scripts filtered to a subset of workspace packages (including only those affected by a change) C Workspaces | developer | Monorepo workspaces — stories about monorepo workspaces in this arenaMonorepo workspaces | 2 | none | 0/10 | ||
Choose where my data is stored (region/residency) G | ai-native user | Privacy posture — data-handling and privacy storiesPrivacy posture | 2 | n/a | untested | none yet | |
Control data retention and deletion G | ai-native user | Privacy posture — data-handling and privacy storiesPrivacy posture | 2 | n/a | untested | none yet | |
Do everything through the API that I can do in the UI G | ai-native user | Openness — open source, data portability, and self-hosting storiesOpenness | 2 | n/a | untested | none yet | |
Opt out of telemetry and usage tracking G | ai-native user | Privacy posture — data-handling and privacy storiesPrivacy posture | 2 | none | untested | none yet | |
Point the manager at private registries or mirrors with scoped authentication C Private registries | platform-engineer | Ecosystem extensibility — stories about ecosystem extensibility in this arenaEcosystem extensibility | 2 | none | untested | none yet | |
Schedule recurring jobs or workflows G | ai-native user | Automation depth — how much of the product can run unattendedAutomation depth | 2 | n/a | untested | none yet | |
Trust that fetched packages are verified against checksums, signatures, or attestations before they run C Integrity | platform-engineer | Security supply chain — stories about security supply chain in this arenaSecurity supply chain | 2 | none | untested | none yet | |
Turn on protections against malicious packages, such as blocking lifecycle scripts or enforcing a minimum release age C Hardening | platform-engineer | Security supply chain — stories about security supply chain in this arenaSecurity supply chain | 2 | none | untested | none yet | |
Point an agent at a documented, text-based lockfile format it can read and diff C Structured output | ai-native user | Agent experience — stories about agent experience in this arenaAgent experience | 1 | partial | 6/10 | Tprobed | |
Have the right tool versions and environment variables activate automatically when I enter a project directory C Environments | developer | Toolchain management — stories about toolchain management in this arenaToolchain management | 1 | partial | 5/10 | Xcommunity | |
See published benchmarks or measured numbers backing the manager's speed claims C Benchmarks | developer | Performance caching — stories about performance caching in this arenaPerformance caching | 1 | none | 0/10 | ||
Extend the manager through third-party taps, overlays, plugins, or backends C Extensibility | developer | Ecosystem extensibility — stories about ecosystem extensibility in this arenaEcosystem extensibility | 1 | none | untested | none yet | |
Version, review, and roll back my automations G | ai-native user | Automation depth — how much of the product can run unattendedAutomation depth | 1 | n/a | untested | none yet |
Opportunities — the stories that would move this product's scores, from its own judged verdictsOpportunitiestop 8 of 25 stories with headroom
What would move uv’s scores — derived from its own judged verdicts, biggest headroom first. Each line quotes what the judge found missing; shipping it (or evidencing it publicly) is the fix.
Security supply chain — stories about security supply chain in this arenaAudit installed dependencies for known vulnerabilities directly from the CLI
nonemoves PA Scoreimpact 30
No evidence pack item mentions vulnerability scanning, CVE auditing, or security advisories in uv's CLI; coverage is entirely about dependency management, tooling, caching, and Python version handling.
Agenticness — how well agents can access and operate the productOperate the product with natural-language commands
nonemoves Built-in AIimpact 30
uv's entire interface is a structured CLI with explicit subcommands (uv init, uv add, uv run, uvx, etc.) documented across the evidence pack; there is no mention of natural-language parsing, an AI assistant, or NL-to-command translation anywhere in the docs or community discussion.
Agenticness — how well agents can access and operate the productBuild against official SDKs
nonemoves agent-readyimpact 30
uv's evidence pack covers CLI commands, docs, and package management features, but there is no mention of an official SDK or programmatic API library that developers could build against for AI-native integration; the closest is the llms.txt documentation index, which is not an SDK.
Agenticness — how well agents can access and operate the productExplore an interactive API reference with runnable examples
nonemoves API qualityimpact 30
uv ships static CLI reference documentation (uv-probe-4) with code-block examples, but there is no interactive, runnable API reference — explicit probes for llms.txt, markdown-doc endpoints, and OpenAPI/Swagger specs all returned 404s (uv-probe-1, uv-probe-2, uv-probe-3), and no evidence describes an interactive playground or executable docs.
Agenticness — how well agents can access and operate the productRely on versioned APIs with a documented deprecation policy
nonemoves API qualityimpact 30
uv is a CLI package manager; the evidence pack shows no versioned API surface, API reference, or documented deprecation policy for such an API — only CLI commands, self-update, and docs indexing are mentioned.
Agenticness — how well agents can access and operate the productDrive the product through a documented public API
partialq5/10moves agent-readyimpact 22.5
Missing: a genuine REST/SDK API, confirmed working llms.txt/openapi endpoint, and evidence of agents driving uv via anything beyond CLI invocation.
Security supply chain — stories about security supply chain in this arenaTrust that fetched packages are verified against checksums, signatures, or attestations before they run
nonemoves PA Scoreimpact 20
No evidence in the pack mentions checksum verification, package signing, or attestation checks before installing/running packages; docs cover caching, tool install, and lockfiles but not supply-chain verification mechanisms.
Install reproducibility — stories about install reproducibility in this arenaEnforce a frozen/immutable lockfile mode that fails the install when the manifest and lockfile disagree
nonemoves PA Scoreimpact 20
The evidence pack confirms uv has a lockfile (uv.lock) and commands like uv add/uv lock --upgrade-package, but nowhere does it mention a --frozen or --locked flag (or any mode) that fails an install when the manifest and lockfile diverge.
Showing the top 8 of 25 — every none/partial verdict in the story verdicts table is headroom.
Think a verdict is wrong? Every verdicts-table row has a Flag link — see the methodology.
Coverage map — which docs area, API section, or community source covers which judged storiesCoverage map5 surfaces · 25 covered stories
Where the cited evidence behind each covered verdict came from — the same citations the verdicts table shows, no extra judging.
Uv docs23 stories
- Have an agent install and update project dependencies non-interactively, with clear exit codes and errors when something fails
- Add, remove, and upgrade dependencies through CLI commands that safely rewrite the manifest and lockfile, so an agent never hand-edits them
- Get machine-readable (JSON) output from core commands so an agent can parse results instead of scraping text
- Point an agent at a documented, text-based lockfile format it can read and diff
- Point an agent at llms.txt or agent-oriented docs
- Run the product headlessly / in CI for automation
- Use an official CLI
- Drive the product through a documented public API
- Download a machine-readable API spec (OpenAPI or equivalent)
- Perform bulk operations across many items at once
- Use the same workflow and config on macOS, Linux, and Windows
- Install almost anything I need from a large, actively maintained package registry or repository
- Bootstrap a fresh clone with one command that installs everything the project declares
- Install dependencies from a lockfile and get the exact same resolved versions on every machine
- Pin exact versions of packages and tools per project and have the manager respect those pins
- Keep using familiar commands and interface conventions from the incumbent tool while adopting this manager
- Migrate an existing project from the incumbent tool with documented import or conversion tooling
- Manage many packages in one monorepo with workspaces sharing a single lockfile and cross-linked local dependencies
- Export all of my data in open formats and leave
- Install prebuilt binary packages from a cache instead of compiling from source
- Make CI installs fast with a documented cache-restore setup and offline-capable installs
- Rely on a shared content-addressable store so the same dependency version is stored once on disk across all projects
- Install and switch language runtimes or tool versions per project from a checked-in config file
Hacker News14 stories
- Have an agent install and update project dependencies non-interactively, with clear exit codes and errors when something fails
- Add, remove, and upgrade dependencies through CLI commands that safely rewrite the manifest and lockfile, so an agent never hand-edits them
- Run the product headlessly / in CI for automation
- Use an official CLI
- Use the same workflow and config on macOS, Linux, and Windows
- Install almost anything I need from a large, actively maintained package registry or repository
- Bootstrap a fresh clone with one command that installs everything the project declares
- Pin exact versions of packages and tools per project and have the manager respect those pins
- Keep using familiar commands and interface conventions from the incumbent tool while adopting this manager
- Migrate an existing project from the incumbent tool with documented import or conversion tooling
- Install prebuilt binary packages from a cache instead of compiling from source
- Make CI installs fast with a documented cache-restore setup and offline-capable installs
- Rely on a shared content-addressable store so the same dependency version is stored once on disk across all projects
- Have the right tool versions and environment variables activate automatically when I enter a project directory
GitHub README6 stories
- Run the product headlessly / in CI for automation
- Use the same workflow and config on macOS, Linux, and Windows
- Pin exact versions of packages and tools per project and have the manager respect those pins
- Read the product's source under an open license
- Have the right tool versions and environment variables activate automatically when I enter a project directory
- Install and switch language runtimes or tool versions per project from a checked-in config file
llms.txt3 stories
Probe proofs — replayable recordings from the probe harnessProbe proofs
Replayable recordings from our probe harness — see the Prove-It protocol to submit one.
$uv --versionreproduced$ uv --version uv 0.12.5 (Homebrew 2026-08-14 aarch64-apple-darwin)
$uv pip install --helpreproduced$ uv pip install --help
Install packages into an environment
Usage: uv pip install [OPTIONS] <PACKAGE|--requirements <REQUIREMENTS>|--editable <EDITABLE>|--group <GROUP>>
Arguments:
[PACKAGE]... Install all listed packages
Options:
-r, --requirements <REQUIREMENTS>
Install the packages listed in the given files
-e, --editable <EDITABLE>
Install the editable package based on the provided local file path
--no-editable
Install any editable dependencies as non-editable [env: UV_NO_EDITABLE=]
--no-editable-package <NO_EDITABLE_PACKAGE>
Install the specified editable packages as non-editable
-c, --constraints <CONSTRAINTS>
Constrain versions using the given requirements files [env: UV_CONSTRAINT=]
--overrides <OVERRIDES>
Override versions using the given requirements files [env: UV_OVERRIDE=]
--excludes <EXCLUDES>
Exclude packages from resolution using the given requirements files [env: UV_EXCLUDE=]
-b, --build-constraints <BUILD_CONSTRAINTS>
Constrain build dependencies using the given requirements files when building source
distributions [env: UV_BUILD_CONSTRAINT=]
--extra <EXTRA>
Include optional dependencies from the specified extra name; may be provided more than
once
--all-extras
Include all optional dependencies
--cert <FILE>
Path to a PEM-encoded CA certificate bundle
--group <GROUP>
Install the specified dependency group from a `pylock.toml` or `pyproject.toml`
--no-deps
Ignore package dependencies, instead only installing those packages explicitly listed on
the command line or in the requirements files
--require-hashes
Require a matching hash for each requirement [env: UV_REQUIRE_HASHES=]
--no-verify-hashes
Disable validation of hashes in the requirements file [env: UV_NO_VERIFY_HASHES=]
--system
Install packages into the system Python environment [env: UV_SYSTEM_PYTHON=]
--break-system-packages
Allow uv to modify an `EXTERNALLY-MANAGED` Python installation [env:
UV_BREAK_SYSTEM_PACKAGES=]
--no-break-system-packages
-t, --target <TARGET>
Install packages into the specified directory, rather than into the virtual or system
Python environment. The packages will be installed at the top-level of the directory
--prefix <PREFIX>
Install packages into `lib`, `bin`, and other top-level folders under the specified
directory, as if a virtual environment were present at that location
--no-build
Don't build source distributions
--no-binary <NO_BINARY>
Don't install pre-built wheels
--only-binary <ONLY_BINARY>
Only use pre-built wheels; don't build source distributions
--python-version <PYTHON_VERSION>
The minimum Python version that should be supported by the requirements (e.g., `3.7` or
`3.7.9`)
--python-platform <PYTHON_PLATFORM>
The platform for which requirements should be installed [possible values: windows, linux,
macos, x86_64-pc-windows-msvc, aarch64-pc-windows-msvc, i686-pc-windows-msvc,
x86_64-unknown-linux-gnu, aarch64-apple-darwin, x86_64-apple-darwin,
aarch64-unknown-linux-gnu, aarch64-unknown-linux-musl, x86_64-unknown-linux-musl,
riscv64-unknown-linux, x86_64-manylinux2014, x86_64-manylinux_2_17, x86_64-manylinux_2_28,
x86_64-manylinux_2_31, x86_64-manylinux_2_32, x86_64-manylinux_2_33,
x86_64-manylinux_2_34, x86_64-manylinux_2_35, x86_64-manylinux_2_36,
x86_64-manylinux_2_37, x86_64-manylinux_2_38, x86_64-manylinux_2_39,
x86_64-manylinux_2_40, aarch64-manylinux2014, aarch64-manylinux_2_17,
aarch64-manylinux_2_28, aarch64-manylinux_2_31, aarch64-manylinux_2_32,
aarch64-manylinux_2_33, aarch64-manylinux_2_34, aarch64-manylinux_2_35,
aarch64-manylinux_2_36, aarch64-manylinux_2_37, aarch64-manylinux_2_38,
aarch64-manylinux_2_39, aarch64-manylinux_2_40, aarch64-linux-android,
x86_64-linux-android, wasm32-pyodide2024, wasm32-pyodide2025, arm64-apple-ios,
arm64-apple-ios-simulator, x86_64-apple-ios-simulator]
--exact
Perform an exact sync, removing extraneous packages
--strict
Validate the Python environment after completing the installation, to detect packages with
missing dependencies or other issues
--dry-run
Perform a dry run, i.e., don't actually install anything but resolve the dependencies and
print the resulting plan
--torch-backend <TORCH_BACKEND>
The backend to use when fetching packages in the PyTorch ecosystem (e.g., `cpu`, `cu126`,
or `auto`) [env: UV_TORCH_BACKEND=] [possible values: auto, cpu, cu132, cu130, cu129,
cu128, cu126, cu125, cu124, cu123, cu122, cu121, cu120, cu118, cu117, cu116, cu115, cu114,
cu113, cu112, cu111, cu110, cu102, cu101, cu100, cu92, cu91, cu90, cu80, rocm7.2, rocm7.1,
rocm7.0, rocm6.4, rocm6.3, rocm6.2.4, rocm6.2, rocm6.1, rocm6.0, rocm5.7, rocm5.6,
rocm5.5, rocm5.4.2, rocm5.4, rocm5.3, rocm5.2, rocm5.1.1, rocm4.2, rocm4.1, rocm4.0.1,
xpu]
--user
Index options:
--index <INDEX>
The indexes to use when resolving dependencies, in addition to the default index [env:
UV_INDEX]
--default-index <DEFAULT_INDEX>
The default package index (by default: <https://pypi.org/simple>) [env: UV_DEFAULT_INDEX]
-i, --index-url <INDEX_URL>
(Deprecated: use `--default-index` instead) The URL of the Python package index (by
default: <https://pypi.org/simple>) [env: UV_INDEX_URL]
--extra-index-url <EXTRA_INDEX_URL>
(Deprecated: use `--index` instead) Extra URLs of package indexes to use, in addition to
`--index-url` [env: UV_EXTRA_INDEX_URL]
-f, --find-links <FIND_LINKS>
Locations to search for candidate distributions, in addition to those found in the
registry indexes [env: UV_FIND_LINKS]
--no-index
Ignore the registry index (e.g., PyPI), instead relying on direct URL dependencies and
those provided via `--find-links`
--index-strategy <INDEX_STRATEGY>
The strategy to use when resolving against multiple index URLs [env: UV_INDEX_STRATEGY=]
[possible values: first-index, unsafe-first-match, unsafe-best-match]
--[redacted]ring-provider <[redacted]RING_PROVIDER>
Attempt to use `[redacted]ring` for authentication for index URLs [env: UV_[redacted]RING_PROVIDER=]
[possible values: disabled, subprocess]
Resolver options:
-U, --upgrade
Allow package upgrades, ignoring pinned versions in any existing output file. Implies
`--refresh`
-P, --upgrade-package <UPGRADE_PACKAGE>
Allow upgrades for a specific package, ignoring pinned versions in any existing output
file. Implies `--refresh-package`
--upgrade-group <UPGRADE_GROUP>
Allow upgrades for all packages in a dependency group, ignoring pinned versions in any
existing output file
--resolution <RESOLUTION>
The strategy to use when selecting between the different compatible versions for a given
package requirement [env: UV_RESOLUTION=] [possible values: highest, lowest,
lowest-direct]
--prerelease <PRERELEASE>
The strategy to use when considering pre-release versions [env: UV_PRERELEASE=] [possible
values: disallow, allow, if-necessary, explicit, if-necessary-or-explicit]
--prerelease-package <PRERELEASE_PACKAGE>
The strategy to use when considering pre-release versions for a specific package
--fork-strategy <FORK_STRATEGY>
The strategy to use when selecting multiple versions of a given package across Python
versions and platforms [env: UV_FORK_STRATEGY=] [possible values: fewest, requires-python]
--exclude-newer <EXCLUDE_NEWER>
Limit candidate packages to those that were uploaded prior to the given date [env:
UV_EXCLUDE_NEWER=]
--exclude-newer-package <EXCLUDE_NEWER_PACKAGE>
Limit candidate packages for specific packages to those that were uploaded prior to the
given date
--no-sources
Ignore the `tool.uv.sources` table when resolving dependencies. Used to lock against the
standards-compliant, publishable package metadata, as opposed to using any workspace, Git,
URL, or local path sources [env: UV_NO_SOURCES=]
--no-sources-package <NO_SOURCES_PACKAGE>
Don't use sources from the `tool.uv.sources` table for the specified packages [env:
`UV_NO_SOURCES_PACKAGE`=]
Installer options:
--reinstall
Reinstall all packages, regardless of whether they're already installed. Implies
`--refresh`
--reinstall-package <REINSTALL_PACKAGE>
Reinstall a specific package, regardless of whether it's already installed. Implies
`--refresh-package`
--link-mode <LINK_MODE>
The method to use when installing packages from the global cache [env: UV_LINK_MODE=]
[possible values: clone, copy, hardlink, symlink]
--compile-bytecode
Compile Python files to bytecode after installation [env: UV_COMPILE_BYTECODE=]
Build options:
-C, --config-setting <CONFIG_SETTING>
Settings to pass to the PEP 517 build backend, specified as `[redacted]=VALUE` pairs
--config-settings-package <CONFIG_SETTINGS_PACKAGE>
Settings to pass to the PEP 517 build backend for a specific package, specified as
`PACKAGE:[redacted]=VALUE` pairs
--no-build-isolation
Disable isolation when building source distributions [env: UV_NO_BUILD_ISOLATION=]
--no-build-isolation-package <NO_BUILD_ISOLATION_PACKAGE>
Disable isolation when building source distributions for a specific package
Cache options:
-n, --no-cache
Avoid reading from or writing to the cache, instead using a temporary directory for the
duration of the operation [env: UV_NO_CACHE=]
--cache-dir <CACHE_DIR>
Path to the cache directory [env: UV_CACHE_DIR=]
--refresh
Refresh all cached data
--refresh-package <REFRESH_PACKAGE>
Refresh cached data for a specific package
Python options:
-p, --python <PYTHON> The Python interpreter into which packages should be installed. [env:
UV_PYTHON=]
--managed-python Require use of uv-managed Python versions [env: UV_MANAGED_PYTHON=]
--no-managed-python Disable use of uv-managed Python versions [env: UV_NO_MANAGED_PYTHON=]
--no-python-downloads Disable automatic downloads of Python. [env:
"UV_PYTHON_DOWNLOADS=never"]
Global options:
-q, --quiet...
Use quiet output
-v, --verbose...
Use verbose output
--color <COLOR_CHOICE>
Control the use of color in output [possible values: auto, always, never]
--system-certs
Whether to load TLS certificates from the platform's native certificate store [env:
UV_SYSTEM_CERTS=]
--offline
Disable network access [env: UV_OFFLINE=]
--allow-insecure-host <ALLOW_INSECURE_HOST>
Allow insecure connections to a host [env: UV_INSECURE_HOST=]
--no-progress
Hide all progress outputs [env: UV_NO_PROGRESS=]
--directory <DIRECTORY>
Change to the given directory prior to running the command [env: UV_WORKING_DIR=]
--project <PROJECT>
Discover a project in the given directory [env: UV_PROJECT=]
--config-file <CONFIG_FILE>
The path to a `uv.toml` file to use for configuration [env: UV_CONFIG_FILE=]
--no-config
Avoid discovering configuration files (`pyproject.toml`, `uv.toml`) [env: UV_NO_CONFIG=]
-h, --help
Display the concise help for this command
Use `uv help pip install` for more details.
$mktemp -d && uv venv && uv pip install requests && uv pip list --format=jsonreproduced$ mktemp -d && uv venv && uv pip install requests && uv pip list --format=json
Using CPython 3.13.15
Creating virtual environment at: .venv
⠋ Resolving dependencies...
⠙ Resolving dependencies...
⠋ Resolving dependencies...
⠙ Resolving dependencies...
⠙ requests==2.34.2
⠙ charset-normalizer==3.5.1
⠙ idna==3.19
⠙ urllib3==2.7.0
⠙ certifi==2026.7.22
⠙
Resolved 5 packages in 1ms
░░░░░░░░░░░░░░░░░░░░ [0/0] Installing wheels...
░░░░░░░░░░░░░░░░░░░░ [0/5] Installing wheels...
░░░░░░░░░░░░░░░░░░░░ [0/5] requests==2.34.2
████░░░░░░░░░░░░░░░░ [1/5] requests==2.34.2
████░░░░░░░░░░░░░░░░ [1/5] urllib3==2.7.0
████████░░░░░░░░░░░░ [2/5] urllib3==2.7.0
████████░░░░░░░░░░░░ [2/5] certifi==2026.7.22
████████████░░░░░░░░ [3/5] certifi==2026.7.22
████████████░░░░░░░░ [3/5] charset-normalizer==3.5.1
████████████████░░░░ [4/5] charset-normalizer==3.5.1
████████████████░░░░ [4/5] idna==3.19
████████████████████ [5/5] idna==3.19
Installed 5 packages in 3ms
+ certifi==2026.7.22
+ charset-normalizer==3.5.1
+ idna==3.19
+ requests==2.34.2
+ urllib3==2.7.0
[{"name":"certifi","version":"2026.7.22"},{"name":"charset-normalizer","version":"3.5.1"},{"name":"idna","version":"3.19"},{"name":"requests","version":"2.34.2"},{"name":"urllib3","version":"2.7.0"}]
Claims vs evidence — vendor claims reconciled against independent verdictsClaims vs evidence
9 of 13 testable claims verified · 0 contradicted → integrity 69/100
32 distinct capability claims found in uv’s own claimed-docs/GitHub materials, reconciled against our judge’s independent verdicts.
9
Verified
4
Unverified
0
Contradicted
12
Undersold
Verified (15)
“Add a dependency to pyproject.toml, updating the lockfile and environment automatically”
Add, remove, and upgrade dependencies through CLI commands that safely rewrite the manifest and lockfile, so an agent never hand-edits themfullproof ↗
“Provides a drop-in replacement CLI for pip, pip-tools and virtualenv commands”
Keep using familiar commands and interface conventions from the incumbent tool while adopting this managerpartialproof ↗
“Upgrade a specific package to the latest compatible version while keeping rest of lockfile intact”
Add, remove, and upgrade dependencies through CLI commands that safely rewrite the manifest and lockfile, so an agent never hand-edits themfullproof ↗
“Official GitHub Action (astral-sh/setup-uv) installs uv, adds to PATH, and can persist cache in CI”
Make CI installs fast with a documented cache-restore setup and offline-capable installspartialproof ↗
“Pin a specific Python version for the current directory/project via `uv python pin`”
Pin exact versions of packages and tools per project and have the manager respect those pinsfullproof ↗
“uv.lock is a documented, cross-platform, text-based lockfile with exact dependency info”
Point an agent at a documented, text-based lockfile format it can read and diffpartialproof ↗
“Invoke a specific pinned version of a tool at run time, e.g. `uvx [email protected]`”
Pin exact versions of packages and tools per project and have the manager respect those pinsfullproof ↗
“Tool upgrades respect the version constraints specified at install time”
Pin exact versions of packages and tools per project and have the manager respect those pinsfullproof ↗
“Uses aggressive caching to avoid re-downloading or re-building already-fetched dependencies”
Make CI installs fast with a documented cache-restore setup and offline-capable installspartialproof ↗
“Disk-space efficient via a global content cache that deduplicates dependencies across projects”
Rely on a shared content-addressable store so the same dependency version is stored once on disk across all projectsfullproof ↗
“Remove a dependency from the project via `uv remove`”
Add, remove, and upgrade dependencies through CLI commands that safely rewrite the manifest and lockfile, so an agent never hand-edits themfullproof ↗
“Migrate an existing project from requirements.txt by importing all deps via `uv add -r`”
Migrate an existing project from the incumbent tool with documented import or conversion toolingpartialproof ↗
“setup-uv action can select Python versions for CI matrix testing across multiple versions”
Make CI installs fast with a documented cache-restore setup and offline-capable installspartialproof ↗
“Commands automatically respect the Python version pinned in the project”
Have the right tool versions and environment variables activate automatically when I enter a project directorypartialproof ↗
“Publishes an llms.txt index and per-page raw markdown docs for agent consumption”
Point an agent at llms.txt or agent-oriented docsfullproof ↗
Unverified (4)
“Installs Python itself and lets you switch between Python versions”
Install and switch language runtimes or tool versions per project from a checked-in config filefullproof ↗
“uv.lock is a documented, cross-platform, text-based lockfile with exact dependency info”
Install dependencies from a lockfile and get the exact same resolved versions on every machinefullproof ↗
“Get machine-readable JSON output from `uv version --output-format json`”
Get machine-readable (JSON) output from core commands so an agent can parse results instead of scraping textpartialproof ↗
“Supports Cargo-style workspaces for managing multiple packages in one project”
Manage many packages in one monorepo with workspaces sharing a single lockfile and cross-linked local dependenciesfullproof ↗
Undersold (12)
Have an agent install and update project dependencies non-interactively, with clear exit codes and errors when something failspartialproof ↗
Run the product headlessly / in CI for automationfullproof ↗
Drive the product through a documented public APIpartialproof ↗
Download a machine-readable API spec (OpenAPI or equivalent)partialproof ↗
Perform bulk operations across many items at oncepartialproof ↗
Use the same workflow and config on macOS, Linux, and Windowsfullproof ↗
Install almost anything I need from a large, actively maintained package registry or repositoryfullproof ↗
Bootstrap a fresh clone with one command that installs everything the project declaresfullproof ↗
Export all of my data in open formats and leavepartialproof ↗
Read the product's source under an open licensepartialproof ↗
Install prebuilt binary packages from a cache instead of compiling from sourcefullproof ↗
Claims outside our story set (14)
Real capability claims found in uv’s own materials, but no story in this arena’s taxonomy covers them yet — that’s feedback on the taxonomy, not a mark against the product.
“Scaffold a new Python project with `uv init`”
source ↗“Run standalone scripts with inline dependency metadata, managing their deps/envs”
source ↗“Acts as a single tool replacing pip, pip-tools, pipx, poetry, pyenv, twine, virtualenv”
source ↗“Run a CLI tool ephemerally in an isolated temp virtual environment via `uv tool run`”
source ↗“Install a CLI tool persistently so its executable is on PATH via `uv tool install`”
source ↗“Clear the entire cache or a specific package's cache with `uv cache clean`”
source ↗“Standalone-installed uv can update itself on demand via `uv self update`”
source ↗“Enable shell autocompletion for uv commands”
source ↗“Include extra packages alongside a tool when running it ephemerally via `uvx --with`”
source ↗“Manages dependencies and isolated environments for single-file scripts”
source ↗“Custom cache-key entries (file paths, git commit hashes) can be configured under tool.uv.cache-keys”
source ↗“Tool environments can be upgraded via `uv tool upgrade` or recreated via reinstall”
source ↗“Add a dependency to a specific standalone script via `uv add --script`”
source ↗“Installable without needing Rust or Python toolchains, via curl or pip”
source ↗
Business model
Free, Apache-2.0/MIT dual-licensed Python package and project manager built by Astral, a venture-funded company that monetizes separately (pyx registry) rather than through uv itself.
pricing ↗Score trend
How this product’s scores have moved as evidence and verdicts are re-derived — a point per change, not per day.
Try Experimental
Run it in the microterminal →Recorded agent sessions — and a live MCP handshake where the vendor ships one.
Flag
⚑ Flag a verdictThink a verdict is wrong? Opens a prefilled GitHub issue — or use the ⚑ next to any verdict above.
For agents